A better, safer normal: Helping you modernize security in the cloud or in place

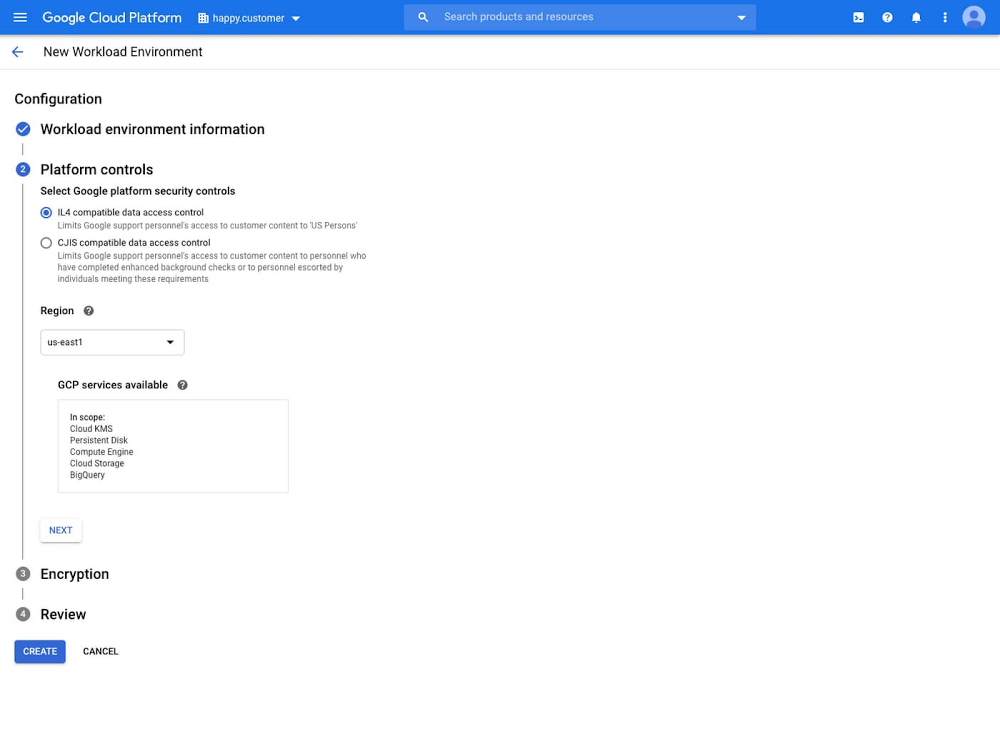
During the first few months of the COVID-19 pandemic, many organizations expected a slowdown in their digital transformation efforts. Instead, we saw many enterprises accelerate their use of cloud-based services to help them manage and address emerging priorities in the new normal, which includes a distributed workforce and new digital strategies. Today, to kick off our Google Cloud Next ‘20: OnAir Security Week, we’re sharing the latest on some unique and powerful capabilities to help you simplify security operations in your organization and make the new normal a better, safer normal. Advanced security tools to support compliance and data confidentiality More and more companies, especially those in regulated industries, want to adopt the latest cloud technologies, but they often face barriers due to strict data privacy or compliance requirements. Last month, we introduced two new capabilities that help you securely take advantage of all the cloud has to offer while also simplifying security operations. Assured Workloads for Government, now in private beta, lets those in regulated industries like the public sector configure and deploy sensitive workloads according to their security and compliance requirements—in just a few clicks. Unlike traditional “government clouds,” Assured Workloads removes the tradeoff between meeting compliance requirements and having the latest capabilities in your cloud.Configuring a new workload in Assured Workloads for GovernmentConfidential VMs, the first product in our Confidential Computing portfolio, helps you protect your sensitive data in the cloud. We already encrypt data at-rest and in-transit, but customer data must traditionally be decrypted for processing. Confidential Computing is a breakthrough technology which encrypts data in-use—while it’s being processed. Confidential VMs takes this technology to the next level by offering memory encryption so that you can further isolate your workloads in the cloud. With the beta launch of Confidential VMs, we’re the first major cloud provider to offer this level of security and isolation while giving you a simple, easy-to-use option for your newly built and “lift and shift” applications.Confidential VMs demoA cloud-based, managed CA for the DevOps and IoT world Recently, we’ve seen a surge in interest in using Public Key Infrastructure (PKI) in DevOps and IoT device management. But a fundamental problem with PKI remains: it’s hard to set up Certificate Authorities (CA), and even harder to do it reliably at scale. These issues are front and center for these growing use cases. To help, we’re announcing the beta availability of Google Cloud’s new Certificate Authority Service (CAS)—a highly scalable and available service that simplifies and automates the management and deployment of private CAs while meeting the needs of modern developers and applications. With CAS, you can offload to the cloud time-consuming tasks associated with operating a private CA, like hardware provisioning, infrastructure security, software deployment, high-availability configuration, disaster recovery, backups, and more, allowing you to stand up a private CA in minutes, rather than the months it might normally take to deploy. A single pane of glass into your security posture Protecting your users, data, and applications while staying compliant can be challenging. Add in the demands of managing a remote workforce and the complexity increases. With Cloud Security Command Center (SCC), our native posture management platform, you can prevent and detect abuse of your cloud resources, centralize security findings from Google Cloud services and partner products, and detect common misconfigurations, all in one easy-to-use platform. We recently announced a Premium tier for Security Command Center to provide even more tools to protect your cloud resources. It adds new capabilities that let you: Spot threats using Google intelligence for events in Google Cloud Platform (GCP) logs and containersSurface large sets of misconfigurations Perform automated compliance scanning and reportingReporting on CIS Benchmarks in the SCC Compliance DashboardThese features help you understand your risks on Google Cloud, verify that you’ve configured your resources properly and safely, and document it for anyone who asks. Collaborating with partners on orchestration and endpointsAs part of our mission to enable operational security and simplicity, we’re committed to working with our security partners to help you on this journey. This week we’re announcing new integrations and go-to-market activities with Palo Alto Networks on their xSOAR Marketplace. Additionally, we’re announcing an expanded partnership with Tanium, which is integrating and offering Chronicle with their endpoint security and management solution. This integrated solution, sold by Tanium, links endpoint data from Tanium with other telemetry, such as DNS and proxy data in Chronicle, to provide a broader, clearer picture of threats in the enterprise. Chronicle retains Tanium telemetry for a year by default, improving your ability to investigate incidents over long periods of time.Simplifying protection against DDoS and web attacksWe’re simplifying how you can use Google Cloud Armor to help protect your websites and applications from exploit attempts, as well as Distributed Denial of Service (DDoS) attacks. With Cloud Armor Managed Protection Plus (in Beta), you will get access to DDoS and WAF services, curated rule sets, and other services for a predictable monthly price. You can learn more about our Cloud Armor announcements here.Automating more secure deployments with blueprintsWhile these new products provide real benefits, you also need to configure cloud deployments to meet your own unique security and compliance requirements. To help, we’re publishing a comprehensive new Google Cloud security foundations blueprint that provides curated, opinionated guidance and accompanying automation to help build a secure starting point for Google Cloud deployments. It’s launching as the cornerstone of our Google Cloud security best practices resource center, a new web destination that delivers world-class security expertise from Google and our partners in the form of security blueprints, guides, whitepapers, and more.A better, safer normal together Defending your enterprise requires continuous evolution, and the events so far in 2020 have made that even more clear. With compliance automation, simpler security operations, and better protection for employees and customers we’re committed to helping you adjust and evolve to make today’s new normal a safer normal. Be sure to check out our security sessions throughout this week where we’ll be digging into the new capabilities we’re introducing, and some we’ve already launched in 2020. You can also find more information at our privacy and security home page.
Quelle: Google Cloud Platform
Introducing CAS: Securing applications with private CAs and certificates

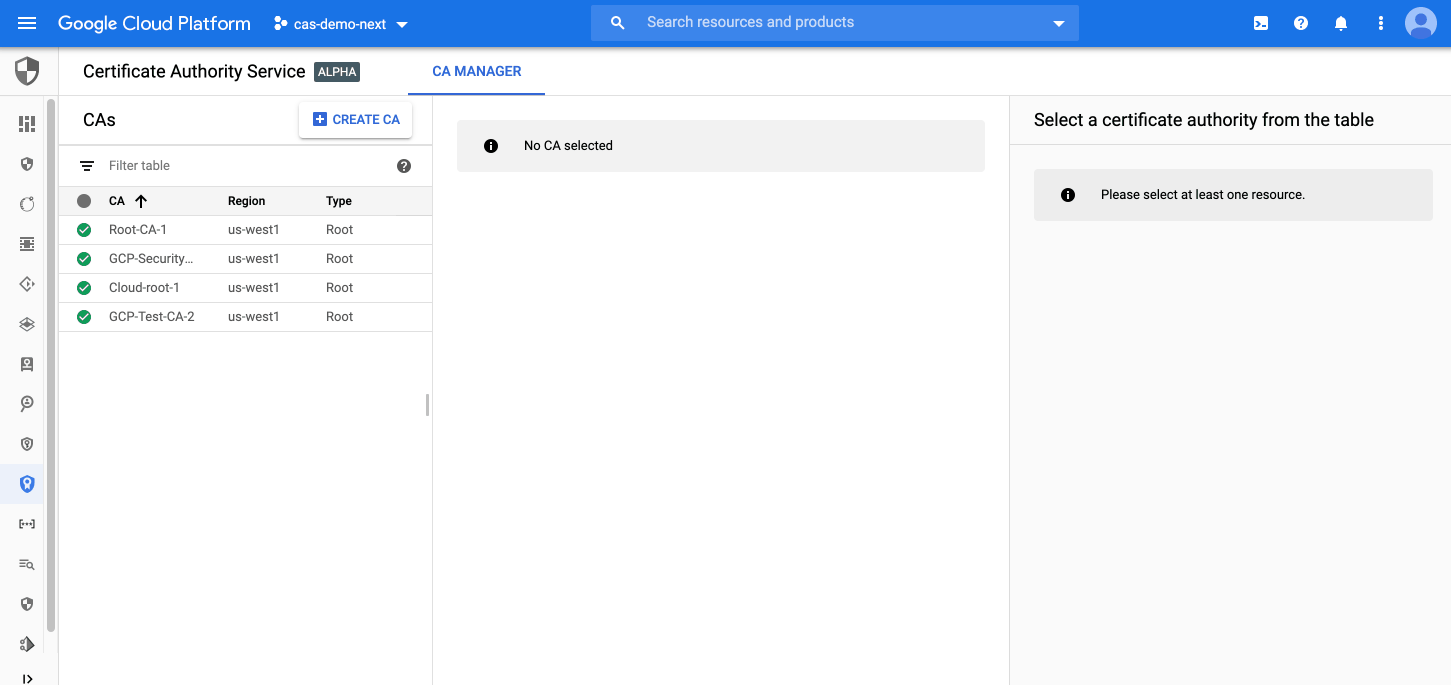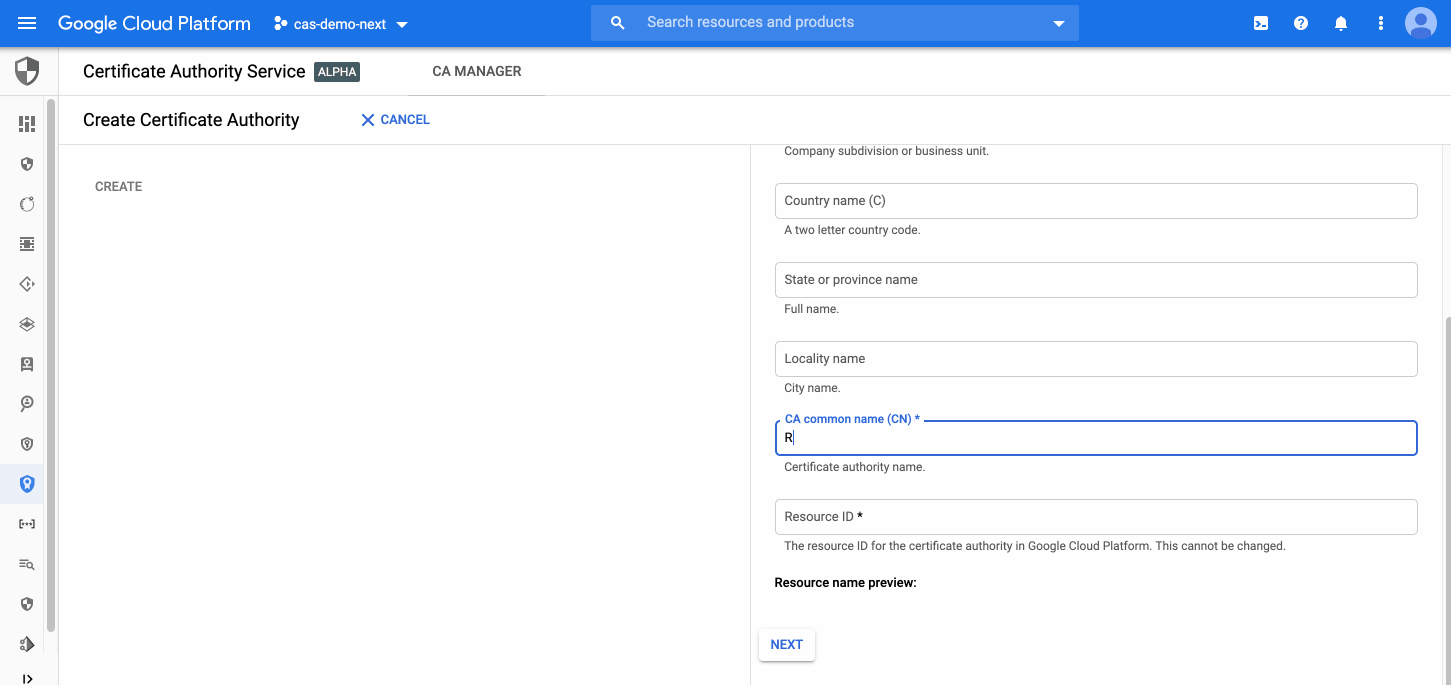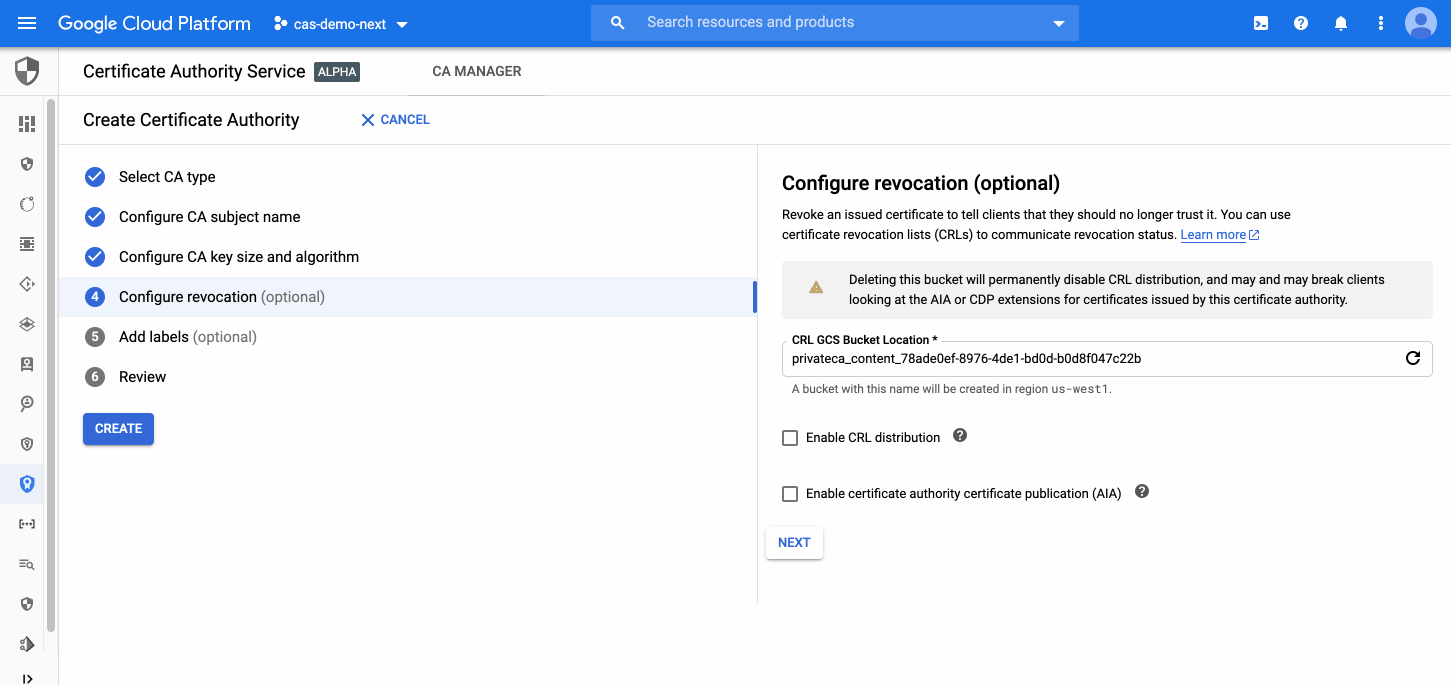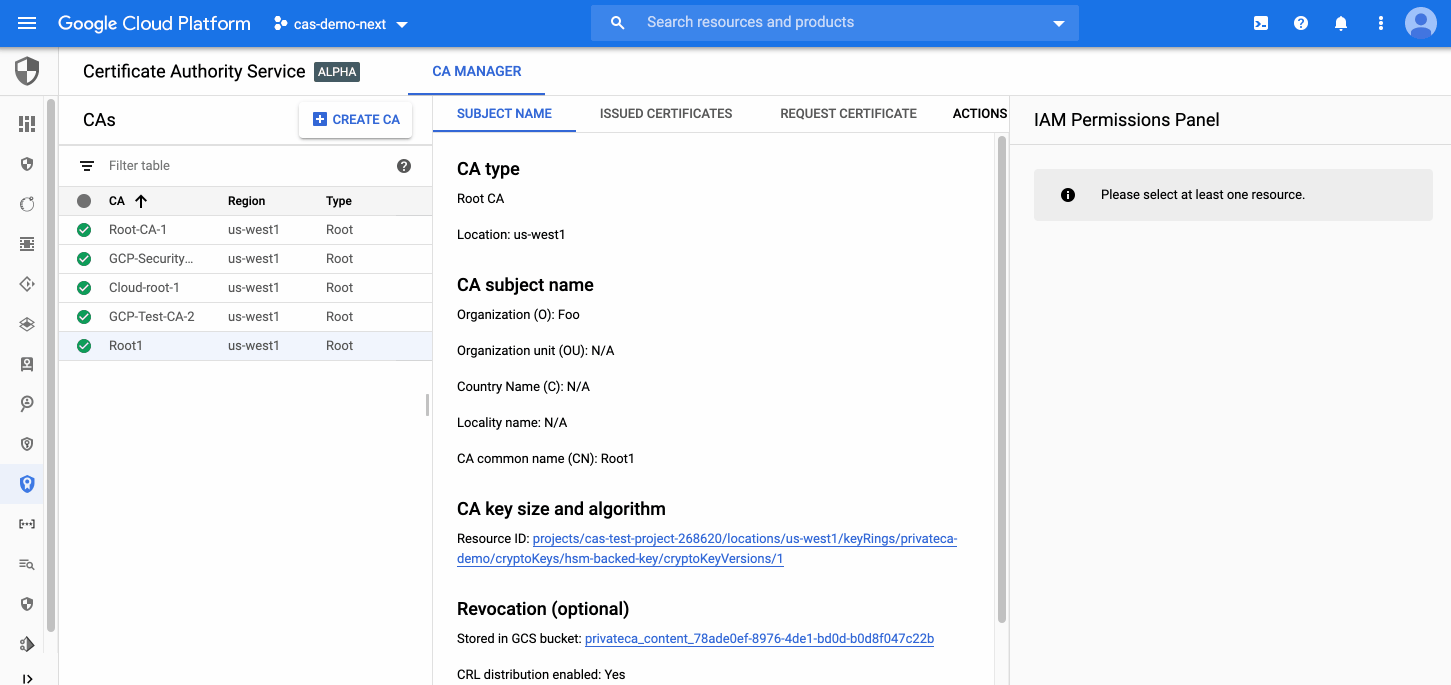
Digital certificates underpin identity and authentication for many networked devices and services. Recently, we’ve seen increased interest in using public key infrastructure (PKI) in DevOps and device management, particularly for IoT devices. But one of the most fundamental problems with PKI remains—it’s hard to set up Certificate Authorities (CA), and even harder to do it reliably at scale. To help, we’re announcing Certificate Authority Service (CAS), now in beta, from Google Cloud—a highly scalable and available service that simplifies and automates the management and deployment of private CAs while meeting the needs of modern developers and applications. To see how CAS can help, let’s look a bit deeper at the challenges surrounding certificate use. As we mentioned, private certificates are one of the most common ways to authenticate users, machines, or services over networks. Digital certificates help make many interactions more secure, including when a user connects to an enterprise-owned website over HTTPS, when a laptop tries to connect to a WiFi access point, or when a user tries to sign into their email account. These certificates are normally issued from a private Certificate Authority (CA) that is hosted on-premises, and they tend to have an expiry date that is in the distant future (i.e., long-lived) with a device/application-specific certificate enrollment process that happens infrequently.An emerging scenario for using private certificates is in DevOps environments to protect containers, microservices, VMs, and service accounts. These emerging private certificate use cases, however, have drastically different requirements. As a result, organizations with an on-premise private CA quickly realize the limitations of their existing private CAs to support these emerging scenarios: These new use cases require short-lived certificates that are renewed frequently, which in turn require high availability and scalability from the CA. Existing private CA solutions fall short. For example, a company may have to issue 10 million certificates in one year vs. 10 thousand when dealing with IoT devices.Certificate enrollment processes do not support modern APIs expected in modern applications and CI/CD toolchains, which result in longer time to market, and delays in adoption and revenue. They are incompatible with cloud providers’ built-in CAs, resulting in customers losing a single point for management and monitoring for certificates. Moreover, organizations that leapfrogged building on-premise infrastructure and were cloud native from day one—i.e., they never had to set up a private CA—started seeing a need for private certificates. Existing on-prem private CAs are not compatible with cloud platforms and can’t support the scale associated with cloud native businesses and hyperscalers. The only option these organizations have is to build their own private CA. Thus, they realize the high cost of setting up and running a private CA (infrastructure, licensing, and operations costs) in addition to the high skill set required to successfully manage a private CA, which is not tied to their core business and only lengthens their go to market timeline. Often, it’s easier and more cost effective to offload this task to a trusted provider—ideally a cloud provider.Certificate Authority Service is designed to meet both traditional and emerging needs. With CAS, you can set up a private CA in minutes, rather than the months it would take to deploy a traditional private CA.Create private CAs in minutesCAS also lets you leverage simple, descriptive RESTful APIs to fully automate the acquisition and management of certificates without being a PKI expert. You can use these APIs for integration with your existing tooling and CI/CD channels. Moreover, you can manage, automate, and integrate private CAs in whichever way is most convenient for you: via APIs, the gcloud command-line, or cloud console.CAS is an enterprise-ready service that enables you to: Store the private CA keys in a Cloud HSM that is FIPS 140-2 Level 3 validated and available in several regions across the Americas, Europe, and Asia Pacific. You can select a subordinate CA’s region independent of its root CA’s regionObtain logs and gain visibility into who did what, when, and where with Cloud Audit LogsDefine granular access controls and virtual security perimeters with Cloud IAM and VPC Service ControlsScale with confidence knowing that the service supports up to 25 queries per second (QPS) per instance (in DevOps mode), which means it can issue millions of certificates. And it comes with an enterprise-grade SLA (at GA)Have assurance that CA private keys are protected by FIPS 140-2 Level 3 validated HSMsBring your own root: This will allow CAs to chain up to an existing root running on-premise or anywhere else outside Google CloudIntegration with the certificate management ecosystemWe also understand that the most important requirement for deploying a new service at an enterprise level is compatibility, with ease-of-use being a close second. After all, security measures that are hard to use end up going unused. We worked with leading partners in the certificate lifecycle management (CLM) space to make sure CAS is integrated with their solutions: Venafi is a leading vendor in machine identity protection with more than 400 worldwide customers and 20-plus years of cybersecurity research and innovation. Venafi’s role has been cited in industry research like Gartner’s 2020 Hype Cycle for IAM and Forester’s 2020 Now Tech report on Zero Trust Solution Providers. For more information on their integration with CAS see their blog.AppViewX CERT+ is a certificate management suite that lets you automate key and certificate lifecycles across multi-cloud environments. It also protects keys, delivers compliance, allows for role-based self-servicing of PKI, and enables hyper scalability and cryptographic agility. For more information on their integration with CAS see their blog.Getting started with CASWith CAS, you can offload time-consuming tasks associated with operating a private CA, like hardware provisioning, infrastructure security, software deployment, high-availability configuration, disaster recovery, backups, and more to the cloud. This will lower your total cost of ownership (TCO) and shorten time to market for your products. CAS also simplifies licensing with pay-as-you-go pricing and zero capital expenditures (CapEx)—you pay only for what you use. During beta availability, you can use CAS at no charge; visit the sign up form to register. Pricing will go into effect once the product is generally available. For more information, check out our product videos and the CAS home page. If you have any questions, just email us at cas-support@google.com.
Quelle: Google Cloud Platform

Session guide: Get the most out of Next OnAir Security Week

With new threats, constantly evolving regulations, and the need to secure increasingly decentralized environments, keeping your organization safe and compliant keeps getting more complex. This year, COVID-19 has impacted all of us in multiple ways—including in how we think about and manage security. Google Cloud Next ‘20: OnAir has a range of sessions on ways we can help secure your organization in today’s new normal. If you haven’t registered yet, no problem. Just head to the Next OnAir website and you’re ready to go. Security week starts with our welcome session where you’ll get an overview of what’s to come. Then, be sure to check out our solution keynote, A Better, Safer Normal, where we’ll look at how you can operate securely and simply in this new security reality we’re facing. This year features over 20 security sessions—all going live at 9am PT on Tuesday, August 4—so there’s sure to be something for every security professional.  Data Protection and Customer ControlsThese sessions provide best practices and tips to help you ensure the confidentiality and privacy of your sensitive data. While they have a focus on encryption and key management options, we’ll also present options for data discovery, classification, and anonymization.Confidential Computing: The Next Frontier In Data Protection: Learn about Confidential Computing and how it’s enabling the shift to private, encrypted services where organizations can be confident that their data stays private and isn’t exposed to cloud providers or their own insiders. Cloud HSM Deep Dive and Best Practices: Cloud HSM has enjoyed fast growth since its 2018 debut. See what’s coming up next in this deep dive.The New World of Controlling Your Data in the Cloud: Cloud External Key Manager and Key Access Justifications: Need to retain tight control over access to your data? Learn more about these products and how they can help you solve your security and compliance challenges.Managing Sensitive Data in Hybrid Environments: Learn how Google Cloud Data Loss Prevention can help you manage data, focusing on support for inspection of content in hybrid environments.Threat Prevention, Detection, and ResponsePreventing threats—whether you’re operating in the cloud, on-prem, or in a hybrid model—is a huge part of almost any security practitioner’s job. Check out these sessions to improve your organization’s threat preparedness.Take Control of Security with Cloud Security Command Center: See how Cloud SCC can help you prevent, detect, and respond to threats in your Google Cloud environment.How You Can Protect Your Web Sites and Applications with Google Cloud Armor: Learn what the latest Cloud Armor announcements mean for you, complete with real-life examples and case studies.Protect Your Customers from Phishing, Malware, Fraud, and Hijacking with Google Cloud User Protection Suite Powered by Google Safe Browsing and reCAPTCHA: Keeping your users safe is job 1. This session shows how you can reduce online fraud with reCAPTCHA Enterprise and the Web Risk API.Scale-Up to Your Security Telemetry: Take an in-depth look at how to use Chronicle, our cloud-native security analytics system built on core Google infrastructure and fed by a massive threat database to be better prepared for threats.Identity & Access ManagementIdentity and access management is one of the key control points in the cloud. These sessions detail the ways you can make sure that the right users have access to the right resources to get their jobs done.Getting Started With BeyondCorp: A Deeper Look into IAP: Check out this session to understand why your company may need to adopt a new, zero-trust security model and how to get started.Using Policy Intelligence to Achieve Least Privilege Access: See how to improve visibility into who has access to what, quickly resolve access control issues, and discover best practices for putting tight controls around your cloud resources to increase security and reduce risk.Uber Presents: Minimizing Permissions Using IAM Recommender: Learn how Uber integrated IAM Recommender with their security hardening pipeline to tighten IAM policies, then look into best practices for improving your IAM without increasing your workload.Advanced IAM: Hacks, Tips, and Tricks for Policy Management: Take a deep-dive into access policy management in IAM, with advanced topics like avoiding policy change conflicts through concurrency control, policy attachment point discovery, client library usage, and more.Deep-Dive: Google Cloud’s Managed Microsoft AD and Applications: Get back on the board for another deep dive, this time into the Google Cloud Managed Service for Microsoft Active Directory.Authentication for Anthos Clusters: Dry off and take a walk through how to authenticate to Anthos clusters, including how to integrate with your identity providers using protocols such as OIDC and LDAP, then check out some hybrid-cloud scenarios to see how to leverage existing authentication tools with Anthos.CollaborationOur productivity and collaboration tools help teams work better together. These sessions will provide you with a blueprint on how G Suite secures your data, and the controls you have to do even more.Keep Hackers Out: A Use-case-led Approach to G Suite Security: Take a deep dive into the security use-cases that customers can solve with G Suite: What do I do if I detect a phishing incident? Looks like a device is compromised, how do I go about remediating? How can I find out who is sharing what outside the organization?No User Left Behind: Empowering Collaboration with Security: Enable seamless security to ensure that G Suite users can access data safely and securely while preserving individual trust and privacy. ComplianceSecurity and compliance are among the first topics that companies face when considering moving workloads to public clouds. These sessions provide the best practices and technology you need to help meet your compliance obligations.Master Security and Compliance in the Public Cloud: Discuss how customers and Google work together to be able to deploy workloads that must meet regulatory and compliance requirements.Building Trust Through Customer Collaboration: Learn how our Cloud Trust team engages with customers to ensure you can confidently adopt our products, whether through pooled audits, contractual commitments, or even a walk through of one of our global data centers.Security, Privacy, and Compliance Solutions for Healthcare: Take a detailed look at how Google Cloud can help healthcare organizations address the many challenges they’re facing and improve the security and governance of their systems while efficiently migrating to the cloud.Mission Possible: Moving Your Most Sensitive Data to GCP: With Assured Workloads, you can move your most sensitive data to Google Cloud while configuring data location controls, administrative access controls, and encryption parameters. Check out this session to learn how.When you’re done with your sessions, be sure to check out the Security Week recap, and keep visiting the blog for more security content.
Quelle: Google Cloud Platform





