Pipistrel: Elektroflugzeug überfliegt Meerenge
Gary Freedman hat als Erster die Cookstraße in Neuseeland mit einem Elektroflugzeug bezwungen. Die Akkuladung hätte fast für den Rückflug gereicht. (Flugzeug, Technologie)
Quelle: Golem

Gary Freedman hat als Erster die Cookstraße in Neuseeland mit einem Elektroflugzeug bezwungen. Die Akkuladung hätte fast für den Rückflug gereicht. (Flugzeug, Technologie)
Quelle: Golem

Mit Android 12 lässt sich beim Casten die Lautstärke eines Chromecast oder smarten Lautsprechers nicht mehr vom Smartphone aus ändern. (Android 12, Sound-Hardware)
Quelle: Golem

Der Computer ist aus dem täglichen Leben nicht wegzudenken. In Hollywood hat man sich schon früh die Frage gestellt: Was, wenn die Maschinen aufbegehren? Von Peter Osteried (Science-Fiction, Computer)
Quelle: Golem

Wegen der Encrochat-Verfahren könnte gar die U-Haftanstalt zu klein werden. Eine Schwerpunktabteilung für die Verfahren soll 2022 starten. (Encrochat, Verschlüsselung)
Quelle: Golem
Red Hat Enterprise Linux (RHEL) 9 Beta is now available, and delivers exciting new features and many more improvements! Let’s take a deeper dive into what’s new and notable.
Quelle: CloudForms
Learn how Red Hat Open Innovation Labs uses an immersive residency to arm customers with the skills, tools, and processes to deliver better software, more quickly, to meet the demands of today’s market.
Quelle: CloudForms
Governments across the globe want to make life easier for their citizens—they want to enable businesses to thrive, increase public safety, and tackle society’s most pressing challenges. Modernizing legacy public sector IT infrastructure is foundational to achieving this, and the right security is a prerequisite for digital transformation. With so much at stake, governments often take direct ownership of defining security requirements and programs to ensure their data is protected in the cloud. In the United States, the FedRAMP and NIST frameworks set the bar for the security of society’s most vital systems—from general administration, to emergency services, to healthcare systems—protecting every citizen and society at large. The weight of this responsibility is reflected in the high bar that must be met to receive FedRAMP High authorization. Google Workspace now is authorized at FedRAMP HighToday, we’re proud to announce that Google Workspace has achieved FedRAMP High authorization. This is a major milestone in our longstanding commitment to serving the needs of the public sector, and to making the world a safer place for everyone. The U.S. federal government has made its ambition for multi-cloud solutions clear, but in many cases has remained strapped to legacy offerings. Having this new choice of a full suite, cloud-first productivity vendor isn’t just a great thing for procurement and security; it also benefits our civil servants, empowering them with access to modern tools and technologies that help them seamlessly connect, create, and collaborate. And with this authorization, our federal customers can access the latest and greatest collaboration and security capabilities that Google Workspace offers without delay. Security is at the forefront of everything we do; it’s infused in every layer of our product design to provide customers with always up-to-date protections against phishing, malware, ransomware, and other cyberattacks. With FedRAMP High authorization across Workspace’s public cloud offering, any customer can rest assured that they are collaborating at this high level of security, without having to purchase and deploy a separate “gov cloud” instance. It also means they can operate seamlessly with relevant government agencies without additional overhead. Additional FedRAMP High authorized products bring Google Cloud capabilities to more public sector agenciesGoogle Cloud continues the steady growth of our catalog of FedRAMP High authorized services, including seven cloud regions. Recently, an additional four new products have also received FedRAMP High authorization, expanding on the authorizations we announced in April:Admin Console is central to building, deploying and scaling applications, along with websites and services—and includes access to Google Cloud’s cloud-native security, plus advanced features in services architecture and data analytics at scale.Cloud Identity is a services-oriented solution to centrally manage both individual users and groups. It enables administrators to manage access and compliance, while ensuring the broadest possible freedom for individuals to work and collaborate, including federated management between Google and other identity providers.Identity and Access Management provides a unified identity, access, app and endpoint management platform for any cloud project. Users gain better and faster access through single sign-on, while multi-factor authentication and endpoint management enables policy enforcement across all devices. Virtual Private Cloud provides managed networking across Google Cloud resources, allowing both the flexibility to scale and assured control of workload connectivity, regionally and globally—without repetitive connectivity and administrative hassles.Google Cloud earns Department of Defense Impact Level 4 Provisional AuthorizationAnother key security standard at the federal level is the Impact Level 4 (IL4) designation, which applies to controlled unclassified information (CUI). Today, we’re proud to announce that Google has earned IL4 authorization from the Defense Information Systems Agency (DISA), allowing CUI to be stored and processed across key Google Cloud services, including our compute, storage and networking offerings, data analytics, virtual private cloud, and identity and access management technologies, when used with Assured Workloads. Unlike other providers, who offer limited authorized services on a small number of isolated “government cloud” regions, Google Cloud has obtained this authorization for our US public cloud regions, ensuring that customers always have access to and seamless compatibility with our latest, most innovative cloud services.The result of substantial engineering work, this authorization will allow organizations who require an IL4 designation, including those in other industries like financial services and healthcare, to be compliant, while taking advantage of Google’s modern cloud technology. The configuration is supported in all seven U.S. regions, and ensures IL4 workloads are supported by U.S. personnel while being stored and processed in the United States. Our new IL4 and FedRAMP authorizations join other Google Cloud data privacy and security features that allow customers to comply with the FBI’s Criminal Justice Information Services (CJIS) standard and the IRS’ Publication 1075 (IRS 1075).Supporting government customers through evolving regulationsExpanding our list of compliance certifications and adding security and compliance resources is a critical part of Google Cloud’s mission to deliver agile, open architectures, unified data and analytics, and leading security solutions—along with productivity tools that support an increasingly hybrid workforce. While these are exciting developments for us, we are most excited about what it means for our public sector customers, who are working hard to achieve their missions and can now use cloud-first solutions to deliver on their mandates.For the latest information on our ongoing compliance efforts across the globe, visit our Compliance Resource Center.
Quelle: Google Cloud Platform
In the public sector, developing new technology requires careful planning—from budgeting, to procurement, to anticipating future software and hardware resources. But even with the best foresight, migrations can be difficult to manage without prior experience working with cloud environments. After all, how can you tell a year in advance what tools your teams will need to address constituent needs? And what if you’re not an expert on cloud systems? In academic research labs, scientists are often asked to spin up research modules in the cloud to create more flexibility and collaboration opportunities for their projects. However, lacking the necessary cloud skills, many projects never get off the ground. Meet RAD Lab, a secure sandbox for innovationThat’s why today we’re introducing RAD Lab, a Google Cloud-based sandbox environment to help technology and research teams advance quickly from research and development to production. RAD Lab is a cloud-native research, development, and prototyping solution designed to accelerate the stand-up of cloud environments by encouraging experimentation with no risk to existing infrastructure. It’s also designed to meet public sector and academic organizations’ specific technology and scalability requirements with a predictable subscription model to simplify budgeting and procurement. With RAD Lab, government agencies, laboratories and university IT departments can quickly create cloud environments for inexperienced and experienced users alike. Teams no longer need to sacrifice simplicity and ease of use for access to the latest, most powerful technologies. With simplified processes and straightforward tools, RAD Lab users can easily spin up projects in just hours. Google Cloud also offers optional workshops to train employees on technology solutions that may be of use in the future. RAD Lab delivers a flexible environment to collect data for analysis, giving teams the liberty to experiment and innovate at their own pace, without the risk of cost overruns. Key features include:Open-source environment that runs on the cloud for faster deployment—with no hardware investment or vendor lock-in.Built on Google Cloud tools that are compliant with regulatory requirements like FedRAMP, HIPAA, and GDPR security policies.Common IT governance, logging, and access controls across all projects.Integration with analytics tools like BigQuery, Vertex AI, and pre-built notebook templates.Best-practice operations guidance, including documentation and code examples, that accelerate training, testing, and building cloud-based environments.Optional onboarding workshops for users, conducted by Google Cloud specialists. RAD Lab is accelerating cloud development for our customers and partnersAs “America’s Innovation Agency,” the U.S. Patent and Trademark Office (USPTO) uses RAD Lab to enable new internal research and development in artificial intelligence/machine learning, data science, enterprise architecture, and more. The agency’s technical specialists and business experts leverage RAD Lab’s sandbox environment to vet ideas and to develop prototypes that can scale.CIO Jamie Holcombe explains, “At the USPTO, we have the privilege to serve American inventors and entrepreneurs—whether they work out of their garages, at Silicon Valley start-ups, or in multinational corporations and research-and-development laboratories. Cloud computing is part of our drive to modernize and transform our agency’s technology to serve that mission. RAD Lab allows our staff—from technical specialists to economists and business experts—to build, test, and validate new cloud solutions to meet critical agency needs.”RAD Lab also provides Google Cloud partners a foundation to deploy tools easier and faster as they deliver cloud-based environments designed for iteration, experimentation, and prototyping to their customers. Jim Coyne, cloud specialist for Health and Life Sciences atOnix, says, “Our customers are looking for a flexible, scalable sandbox environment to trial different solutions and applications, and see what works best for them. RAD Lab gives us the flexibility to work with our customers to innovate with Google Cloud in entirely new ways.” Girish Reddy, CTO of SpringML, says, “We are excited to use RAD Lab to deliver Google Cloud tools to our customers in an accessible, open-source environment. It’s an invaluable tool in helping customers adopt AI/ML solutions and show them the power of their own data.” Start experimenting now to make more progress fasterWith the rapid deployment of RAD Lab, your teams can be up-and-running and prototyping cloud deployments in hours, rather than weeks or months. In the public sector and other regulated industries, we can help you determine the best cloud capabilities to include in your RAD Lab deployment, ensuring your teams have access to the technology they need when they need it. Contact your Google Cloud team to scope your own RAD Lab projects, or apply now for free research credits in select countries.
Quelle: Google Cloud Platform
The Air Force Research Laboratory (AFRL) is a global research enterprise supporting two services, the U.S. Air Force and the U.S. Space Force. From laser-guided optics enabling telescopes to see deeper into the universe to fundamental science that has spawned innovations in quantum computing and artificial intelligence, AFRL rapidly scales discovery to deliver leading-edge technologies for the military. As an integral part of the nation’s defense, AFRL engages with world-leading scientists, small businesses, large industry, and other government agencies to build communities that drive innovation. And given the sensitive nature of its work, AFRL needs to maintain high levels of security, even with remote employees. To tackle these challenges, AFRL is deploying Google Workspace among a segment of its workforce of scientists and engineers. A single, secure platform for collaboration and innovationAs a leader in developing cutting-edge technology, AFRL needs flexibility, but also must meet rigorous security standards—while maintaining the agility to onboard new researchers quickly. AFRL teams are using Google Workspace solutions like Google Smart Canvas to simultaneously share, collaborate, and discuss research—eliminating the toil of email chains and hours-long data file exchanges. Through video conferencing service, Google Meet, some AFRL research teams are hosting flexible, virtual meetings to exchange ideas anywhere, anytime. The recent announcements of Workspace Client-Side Encryption, combined with Google’s Zero Trust security approach, provides AFRL additional safeguards, while keeping security measures invisible to end-users. Ultimately, the goal is to accelerate collaboration and innovation amongst AFRL scientists, while meeting the standards defined by the U.S. Defense Information Systems Agency (DISA).“Covid-19 significantly limited the physical presence of researchers in the lab,” said Dr. Joshua Kennedy, research physicist, Materials and Manufacturing Directorate at AFRL. “Google Workspace eliminated what would have otherwise been almost a total work stoppage. In fact, new insights into 2D nanomaterials, critical to future Department of the Air Force capabilities, were discovered using Workspace that would have otherwise been impossible.” Dr. Kennedy is just one of many researchers at AFRL who have reported a positive, tangible impact on their work as a result of using Google Workspace. For example, a recent survey of hundreds of researchers involved in the Google Workspace preliminary deployment revealed an average time savings of three hours per week. For AFRL’s highly trained workforce of PhDs, that means more time to dedicate to the mission.Secure collaboration for a global missionAFRL’s global workforce fuels the organization’s innovations, but its worldwide footprint is the source of one of its biggest challenges: How do you create a collaborative, secure, and adaptive environment for an advanced research organization without hampering its ability to innovate?In early fiscal year 2021, Air Force Research Laboratory commander Maj. Gen. Heather Pringle directed AFRL to prioritize ongoing efforts of digitally transforming AFRL and issued a charter establishing the AFRL Digital Transformation Team. The team’s charter outlines the vision of “One AFRL”—a flexible, synergistic enterprise “that capitalizes on the seamless integration of data and information through the use of modern methods, digital processes and tools and IT infrastructure.”“Our mantra is ‘collaborate to innovate,’” Pringle said. “We want our alpha nerds to be very connected, and we really want to up their proficiency as a digital workforce where data becomes a third language. We’re incorporating digital engineering into everything we do in science and technology and have a data-informed human capital strategy. We started experimenting with Google Workspace to supplement existing capabilities, and it has revolutionized our ability to collaborate with our external partners and build the best teams.”Learn more about how Google Cloud has worked with the U.S. Air Force to solve its toughest sustainment challenges and how Google Cloud is helping the Air Force transform future pilot training.
Quelle: Google Cloud Platform
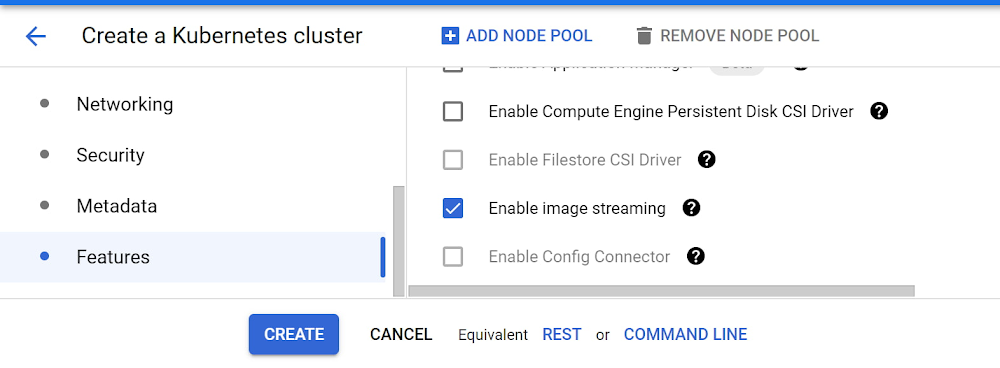
We’re excited to announce the general availability of a new feature in Google Kubernetes Engine (GKE): image streaming. This revolutionary GKE feature has the potential to drastically improve your application scale-up time, allowing you to respond to increased user demand more rapidly, and save money by provisioning less spare capacity. We achieve this by reducing the image pull-time for your container from several minutes (in the case of large images) to a couple of seconds (irrespective of container size), and allowing your application to start booting immediately while GKE streams the container data in parallel.The way Kubernetes traditionally works when scaling up your application is that the entire container image must be downloaded onto the node before the application can boot. The bigger your container image, the longer this takes, despite the fact that most applications don’t actually need every byte of data in the container image to start booting (and some data in the container may even never be used). For example, your application may spend a bunch of time connecting to external databases, which barely requires any data from the container image. With image streaming, we asked ourselves, what if we could deliver to your application just the data it needs, when it needs it, rather than waiting for all that extra data to be downloaded first?Image streaming works by mounting the container data layer in containerd using a sophisticated network mount, and backing it with multiple caching layers on the network, in-memory and on-disk. Your container transitions from the ImagePulling status to Running in a couple of seconds (regardless of container size) once we prepare the image streaming mount; this effectively parallelizes the application boot with the data transfer of required data in the container image. As a result, you can expect to see much faster container boot times and snappier autoscaling. Image streaming performance varies, as it is highly dependent on your application profile. In general, though, the bigger your images, the greater the benefit you’ll see. Google Cloud partner Databricks saw an impressive reduction in overall application cold-startup times, which includes node boot-time.“With image streaming on GKE, we saw a 3X improvement in application startup time, which translates into faster execution of customer workloads, and lower costs for our customers by reducing standby capacity.” – Ihor Leshko, Senior Engineering Manager, DatabricksIn addition to parallelizing data delivery, GKE image streaming employs a multi-level caching system: It starts with an in-memory and on-disk cache on the node, and moves up to regionally replicated Artifact Registry caches designed specifically for image streaming which leverage the same technology as Cloud Spanner under the hood.Image streaming is completely transparent as far as your containerized application is concerned. Since the data your container reads is initially streamed over the network, rather than from the disk, raw read performance is slightly slower with image streaming than when the whole image is available on the disk. This effect is more than offset during container boot by the parallel nature of the design, as your container got a lengthy head start by skipping the whole image pull process. However, to achieve equal read performance once the application is running, GKE still downloads the complete container image in parallel, just like before. In other words, while GKE is downloading the container image, you get the parallelism benefits of image streaming; then, once it’s downloaded, you get the same on-disk read performance as before—for the best of both worlds.Getting started with GKE image streamingImage streaming is available today at no additional cost to users of GKE’s Standard mode of operation, when used with images from Artifact Registry, Google Cloud’s advanced registry for container images and other artifacts. Images in Container Registry, or external container registries, are not supported for image streaming optimization (they will continue to work, just without benefiting from image streaming), so now is a great time to migrate them to Artifact Registry if you haven’t already.You can use image streaming on both new and existing GKE clusters. Be sure to enable the Container Filesystem API, use the COS containerd node image variant, and reference container images that are hosted in Artifact Registry. In the UI, simply check the “enable image streaming” checkbox on the cluster creation page.Alternately, from the CLI, here’s how to create an image streaming cluster:You can also upgrade your existing clusters to enable image streaming through the UI, or by running:and then deploy your workload referencing an image from Artifact Registry. If everything worked as expected, you should notice your container entering the “Running” status about a second after the “ContainerCreating” status.To verify that image streaming was engaged as expected, runThe ImageStreaming event as seen in the example output above indicates that image streaming was engaged for this image pull.Since image streaming is only used until the image is fully downloaded to disk, you’ll need to test this on a fresh node to see the full effect. And remember, to get image streaming, you need to enable the API, turn on image streaming in your cluster, use the COS containerd image, and reference images from Artifact Registry. Image streaming does introduce an additional memory reservation on the node in order to provide the caching system, which reduces the memory available for your workloads on those nodes. For all the details, including further information on testing and debugging, check out the image streaming documentation. For more such capabilities register to join us live on Nov 18th for Kubernetes Tips and Tricks to Build and Run Cloud Native Apps.
Quelle: Google Cloud Platform






