AWS startet ein neues Programm zur Steuerung von Migrationen für Windows Server-Anwendungen, die nicht mehr unterstützt werden

AWS hilft Kunden bei der Migration ihrer alten Windows Server-Anwendungen auf die neuesten unterstützten Versionen von Windows Server auf AWS ohne Code-Änderungen. Viele Unternehmen haben Schwierigkeiten bei der Migration ihrer Legacy-Anwendungen aufgrund der engen Abhängigkeiten von älteren, nicht unterstützten Betriebssystemen, des begrenzten internen Fachwissens und/oder des fehlenden Zugriffs auf Installationsmedien oder Quellcode. Außerdem verhindert der Erwerb von verlängertem Support für diese Anwendungen nicht die unausweichliche Einstellung des Supports und zögert das Unvermeidliche nur hinaus. Zur Überwindung dieser Herausforderungen bietet AWS das End-odf-Support Migration Program (EMP) for Windows Server.
Quelle: aws.amazon.com

Neue AWS Deep Learning AMIs mit aktualisierter Framework-Unterstützung: Tensorflow 1.15 & 2.0, PyTorch 1.3.1 und MXNet 1.6.0-rc0

Die AWS Deep Learning AMIs sind auf Ubuntu 18.04, Ubuntu 16.04, Amazon Linux 2 und Amazon Linux mit TensorFlow 1.15, Tensorflow 2.0, PyTorch 1.3.1, MXNet 1.6.0-rc0 verfügbar. Ebenfalls neu in dieser Version ist die Unterstützung für AWS Neuron, ein SDK zur Ausführung von Inferenz mit AWS Inferentia Chips. Die Chips bestehen aus Compiler, Laufzeit- und Profilerstellungstools, die es Entwicklern ermöglichen, hochleistungsfähige und latenzarme Inferenz-Workloads auf Inferentia-basierten EC2 Inf1-Instances auszuführen. Neuron ist in gängige Frameworks für Machine Learning wie TensorFlow, Pytorch und MXNet bereits integriert, um eine optimale Leistung der EC2 Inf1-Instances zu gewährleisten. Kunden, die Amazon EC2 Inf1 Instances nutzen, erhalten die höchste Leistung bei niedrigsten Kosten für Machine Learning Inferenzen in der Cloud und müssen nicht mehr den ungünstigen Kompromiss zwischen Latenzoptimierung oder Durchsatz eingehen, wenn sie große maschinelle Lernmodelle ausführen.  
Quelle: aws.amazon.com

Wir stellen vor: die Amazon EventBridge Schema Registry – jetzt in der Vorschauversion

Die Amazon EventBridge Schema Registry speichert Ereignisstrukturen – oder Schemas – an einer gemeinsamen zentralen Stelle und ordnet diese Schemas dem Code für Java, Python und Typescript zu, was Ihnen die Verwendung von Ereignisse als Objekte in Ihrem Code wesentlich erleichtert. Schemas aus Ihrem Event Bus werden, wenn Sie die Schema-Erkennung aktivieren, automatisch zur Registry hinzugefügt. Sie können sich mit der Schema Registry über die AWS-Konsole, APIs oder die SDK-Toolkits for JetBrains (Intellij, PyCharm, Webstorm, Rider) und VS Code verbinden und mit ihr interagieren.
Quelle: aws.amazon.com

Der AWS License Manager ermöglicht es Administratoren, die Erkennung bestehender Softwarelizenzen zu automatisieren

Der AWS License Manager ermöglicht es Administratoren nun, die Erkennung der BYOL-Nutzung (Bring Your Own License) in ihren AWS- und On-Premises Umgebungen zu automatisieren. Mit wenigen Klicks können Administratoren nun Produktinformationen und Lizenzregeln für BYOL-Software angeben. Auf diese Weise kann der Lizenzmanager automatisch die Instanzen verfolgen, auf denen die angegebene Software installiert ist, und den Administrator über Verstöße gegen die Lizenzregel informieren. Administratoren bleiben so über alle Softwareinstallationen in ihrer Umgebung auf dem Laufenden und können eine Nutzung verhindern, die nicht mit Ihren definierten Lizenzregeln übereinstimmt. 
Quelle: aws.amazon.com

Enabling a more secure cloud with our partners

Security is top of mind for every organization, at every stage of your cloud journey, whether you’re just beginning to migrate a few applications or running entire stacks of mission-critical workloads in the cloud.At Google Cloud, we think of security through three lenses: Security of the cloud—Providing a highly secure foundation to build on. Security in the cloud—Helping to make sure your apps and data are better protected against threats with advanced and easy to use tools. Security beyond our cloud—Using solutions like Chronicle powered by Google Cloud infrastructure to help you protect your systems wherever they may reside, be that on-premises or in other clouds.We understand that many customers have dedicated tools and strategic relationships with the industry’s leading security vendors. We want to meet you where you are, allowing you to preserve your investments, as well as benefit from functionality you can’t get on other clouds. That’s why we work closely with partners in the security industry to help you better secure your applications and information.Today, we are excited to announce more than a dozen new solutions and security partner integrations with Google Cloud that further advance our capabilities. These include:Launching a new solution to help customers manage the deployment of agent-based endpoint security and vulnerability management solutions, automatically and at scale, with McAfee, Palo Alto Networks, and Qualys on Google Cloud.Growing our strategic partnership with Palo Alto Networks to expand its usage of services on Google Cloud and to jointly develop new solutions for Anthos and threat detection.Announcing a new strategic partnership with McAfee to integrate its MVISION Cloud solution for data security, threat prevention, governance, and compliance capabilities for container workloads with Google Cloud, as well as its endpoint security solution for Linux and Windows based workloads.The availability of Citrix Workspace for customers on Google Cloud. This includes integration with G Suite that provides a single sign-on experience, multi-factor authentication, enhanced security policies for G Suite, web filtering policies for G Suite, and end-to-end visibility and analytics. Also, users will be able to seamlessly authenticate using G Suite credentials early next year to provide simple, secure access to the apps and information they need to do their jobs anywhere, on any device.Exabeam, a leading SIEM vendor, will expand its SaaS Cloud security management platform on Google Cloud, helping customers bring the scale and speed of the cloud to their existing, trusted SIEM platform.A new strategic partnership with ForgeRock to deliver its Digital Identity Platform on Google Cloud. ForgeRock’s platform helps customers build and maintain cloud-ready architecture to automate multi-cloud deployments. ForgeRock joins Google Cloud as a Premier Partner in the identity space and has named Google Cloud as its primary cloud provider for its cloud-native suite of identity products.Expanding our work with Fortinet to provide a new reference architecture for customers to connect facilities to Google Cloud with secure SD-WAN solutions, to make its FortiWeb Cloud WAF-as-a-Service available on Google Cloud, and to integrate its FortiCWP service with Google Cloud Security Command Center.New support from Semperis and STEALTHbits to enable customers to manage, audit, and protect their Microsoft Active Directory-dependent apps and workloads running on Google Cloud from service outages, data breaches, and cyberattacks.A new integration between Tanium’s endpoint security telemetry and Chronicle’s Backstory platform to provide full visibility into endpoint events across an enterprise.Many customers today also work with security service providers to help them implement the right solutions for their businesses. To help simplify implementation and management, we are expanding our work with leading systems integrators and managed services providers, including:Deloitte is expanding its work with Google Cloud to provide customers with end-to-end risk mitigation services and solutions to combat cyber threats across their cloud services. New offerings include security monitoring and threat response solutions to detect and respond to unauthorized activity before it can adversely affect a customer’s network; “zero trust” solutions to provide around-the-clock risk assessments of users; identity and access management services; and data security solutions to help organizations assess potential risks and develop a data risk governance program.IBM Security will provide consulting and managed services for Google Cloud customers to help develop, enforce, and manage security and compliance policies across public-, hybrid-, and multi-cloud environments.Wipro, the global IT consulting firm, will deliver new security services for Google Cloud customers, including consulting, digital transformation, architecture design, security controls configuration, and continuous controls management.Arctic Wolf, a leading security operations center-as-a-service provider, will make their managed detection and response services available for Google Cloud customers to provide centralized and continuous monitoring of user and application activity across a customer’s entire cloud deployment.Comm-IT, a leading security systems integrator, will extend support to Google Cloud customers, providing a single, unified view of security risks across cloud deployments.Cyderes, a managed security service provider, is adding full support for Chronicle Backstory to analyze massive amounts of security telemetry without the need for additional hardware, maintenance, tuning, or ongoing management. Optiv will partner with Google Cloud to deliver new solutions to reduce security risks as customers move to the cloud. Optiv will expand the availability of its Security Architecture Assessment Services for Google Cloud to global customers, and will bring new services to Google Cloud for identity management, device management, and data management.In addition, we are excited to recognize several partners who partnered with Google Cloud to build specialized security solutions and demonstrated high levels of success in meeting customer needs. This first set of partners includes Aqua, Cavirin, Check Point Software Technologies, Fortinet, McAfee, Palo Alto Networks, and Qualys.At Google Cloud, we’re committed to providing customers with high levels of security and data protection. It’s why leading security companies chose to run their own products on our cloud. Today’s announcements further build on this commitment to our customers, and we look forward to continued collaboration with our partner ecosystem to enable advanced security capabilities. Learn more about security on Google Cloud.
Quelle: Google Cloud Platform

Availability, scale, and ease of management with new Layer-4 Internal Load Balancing features

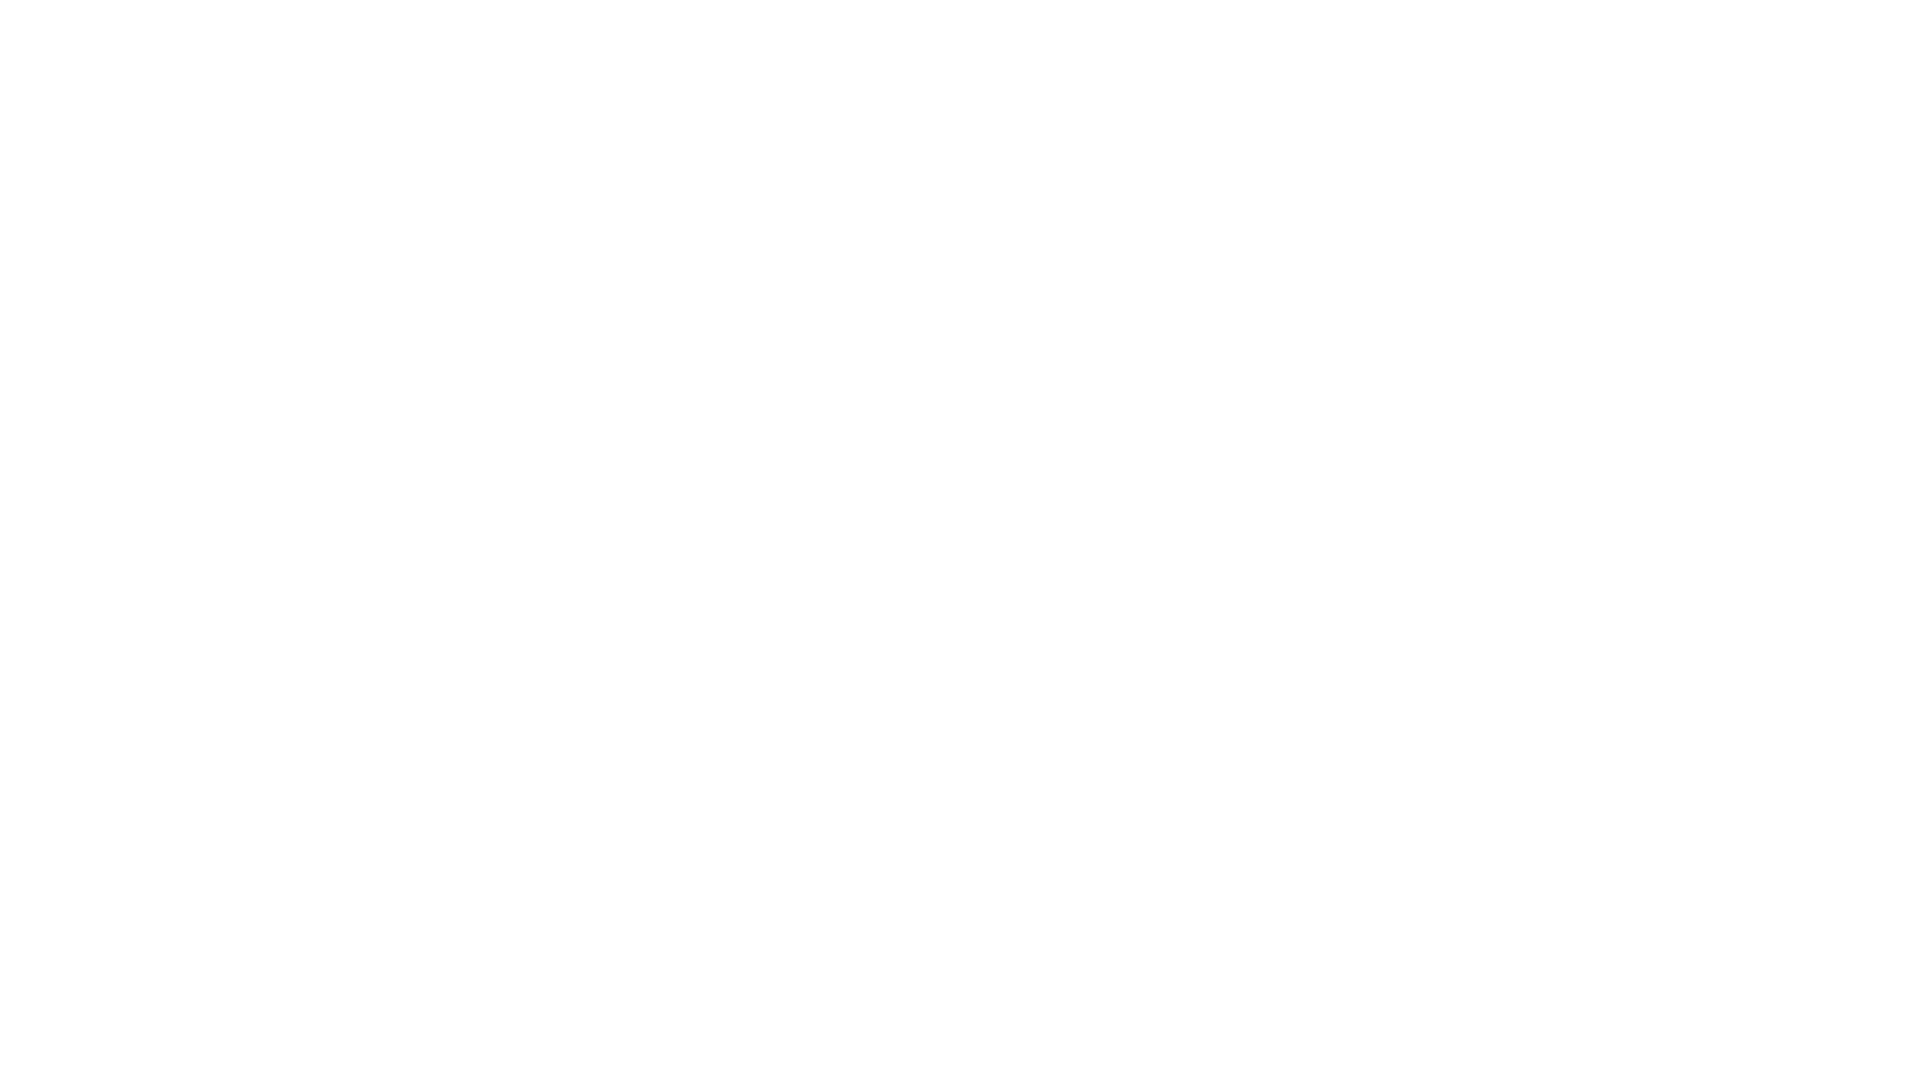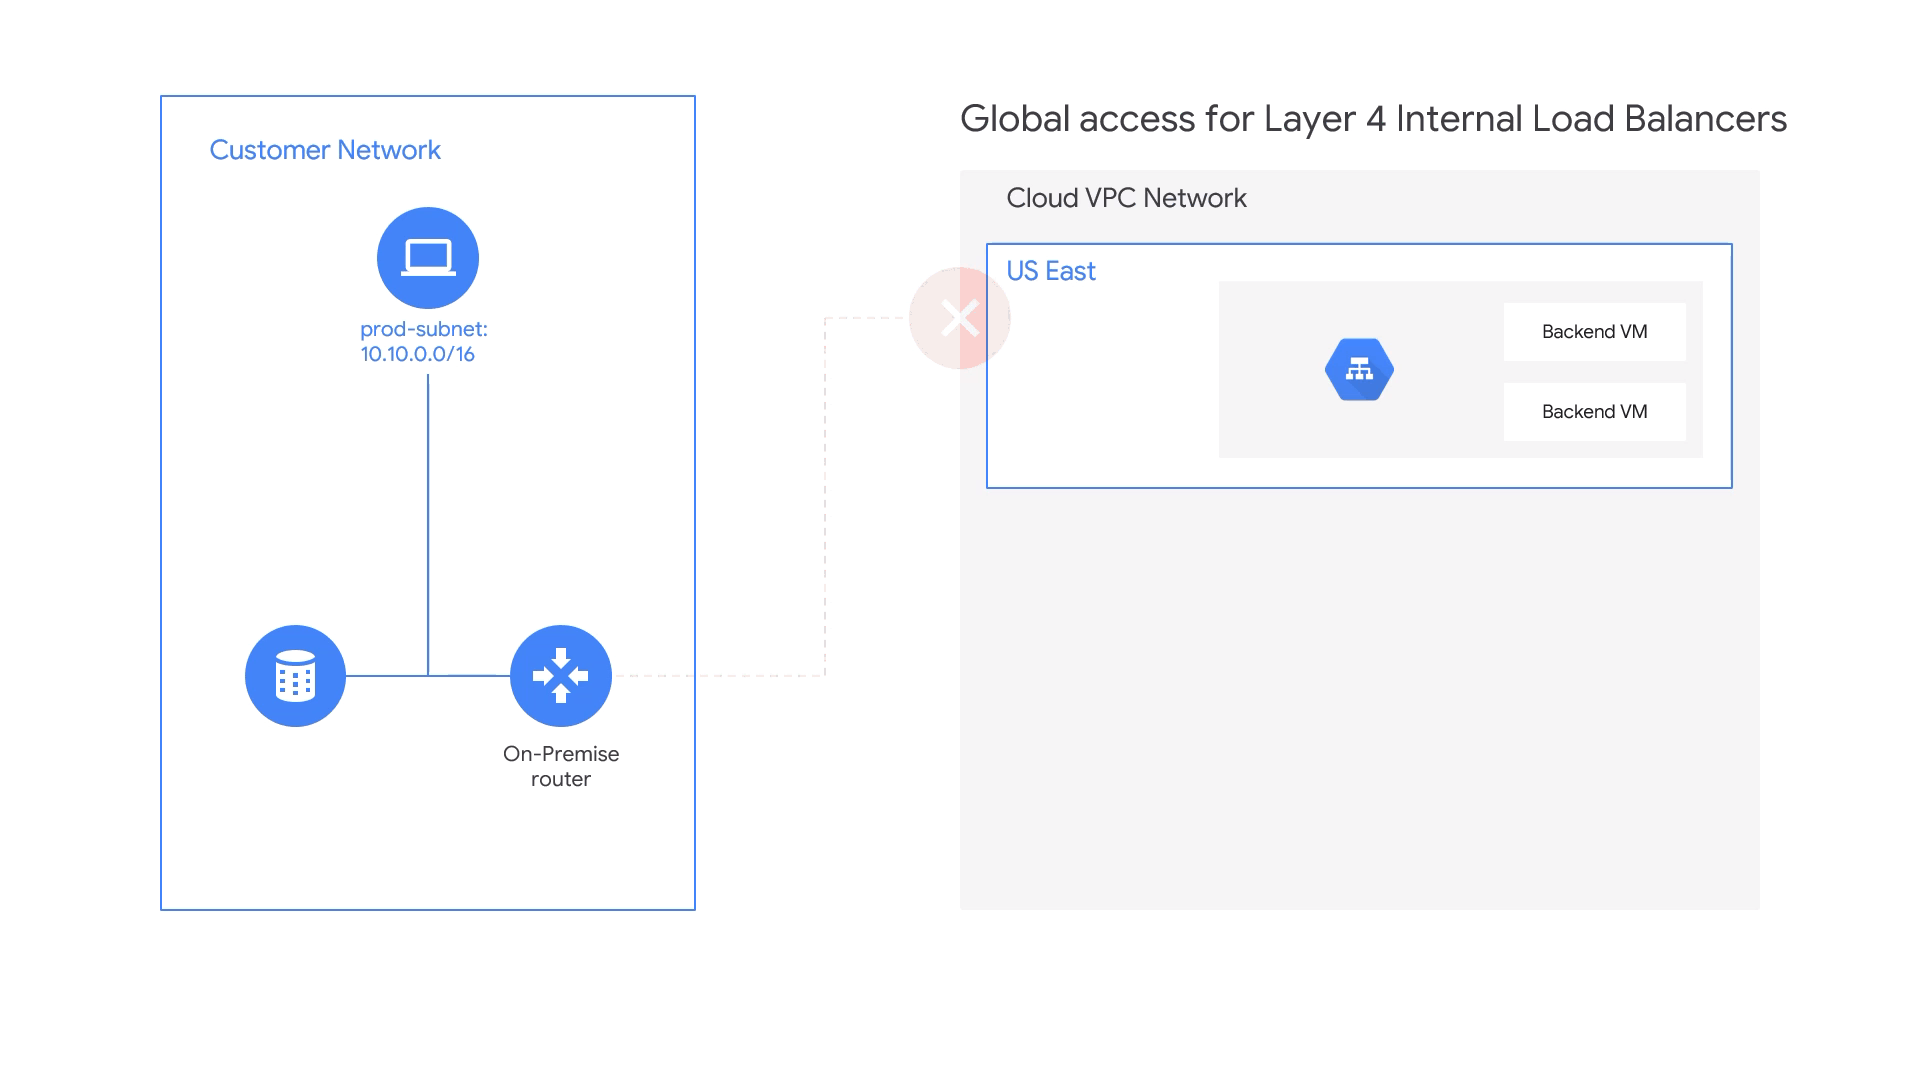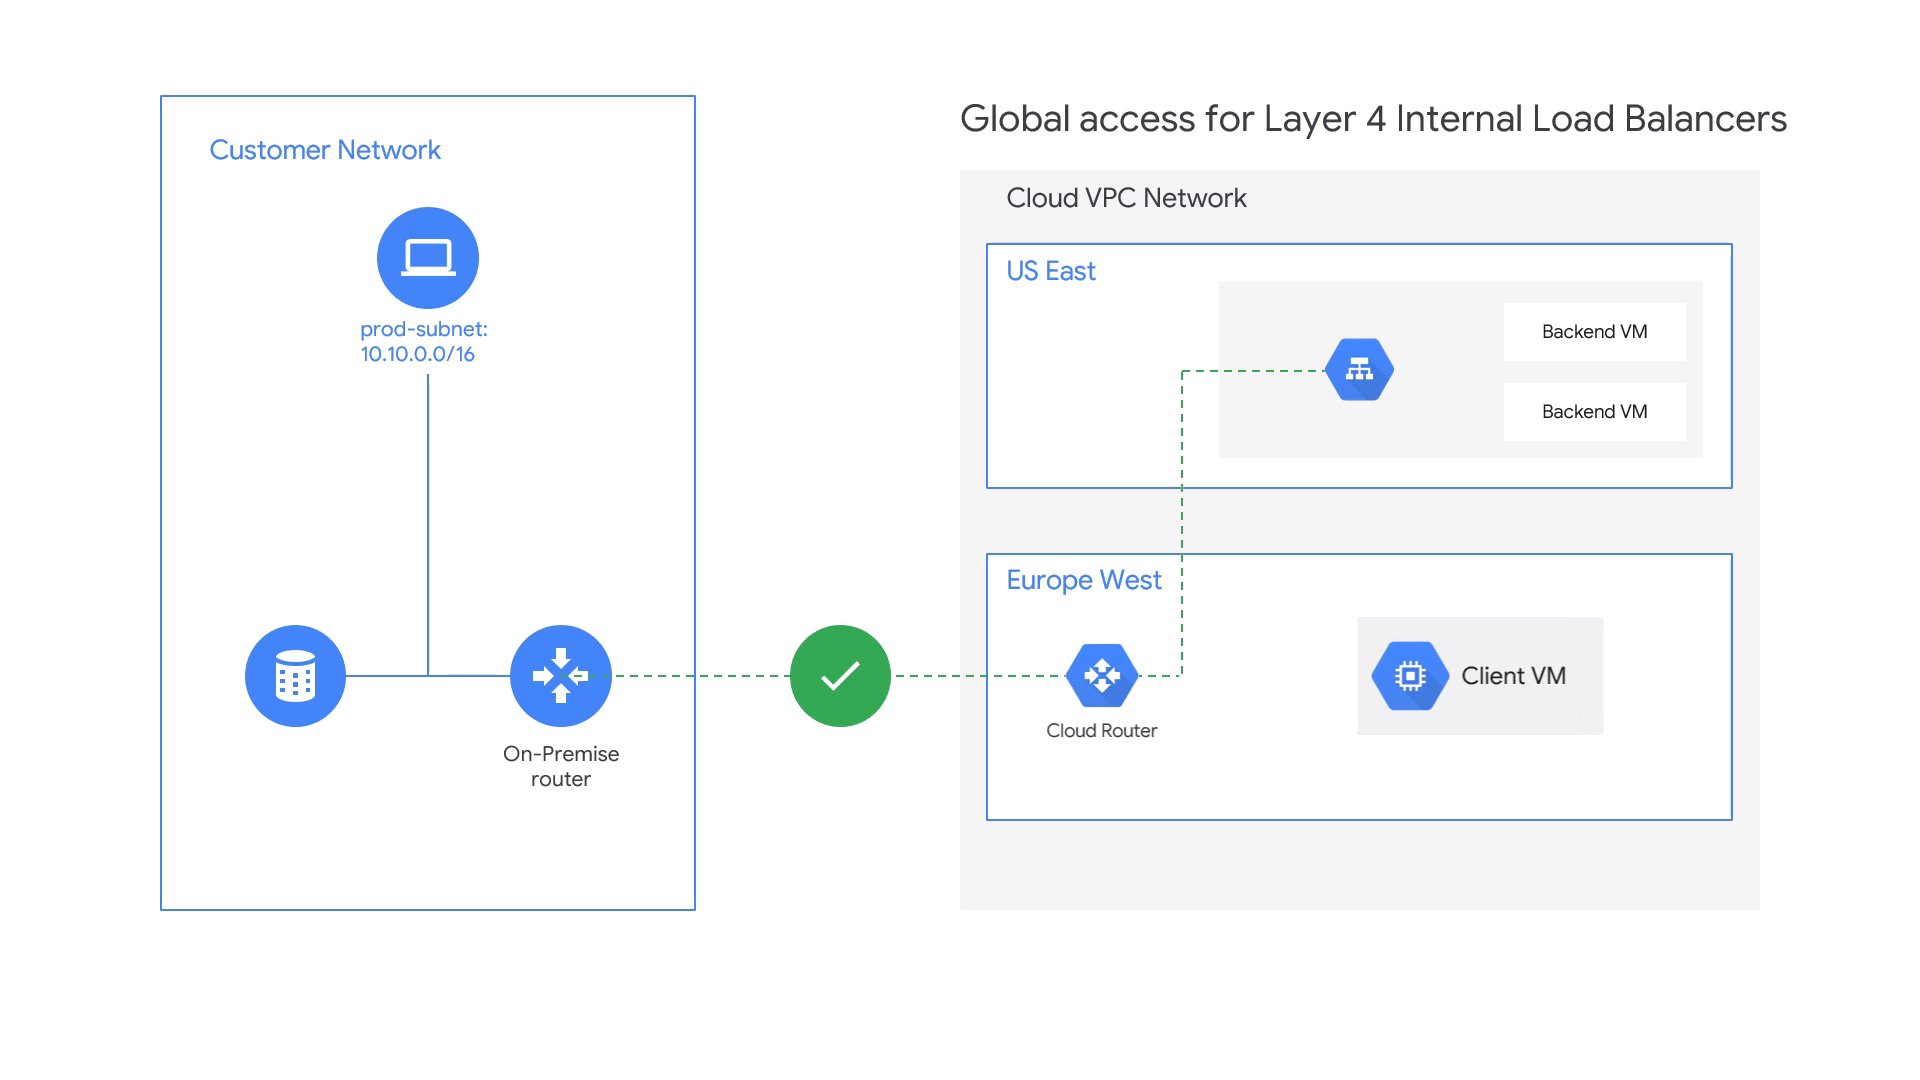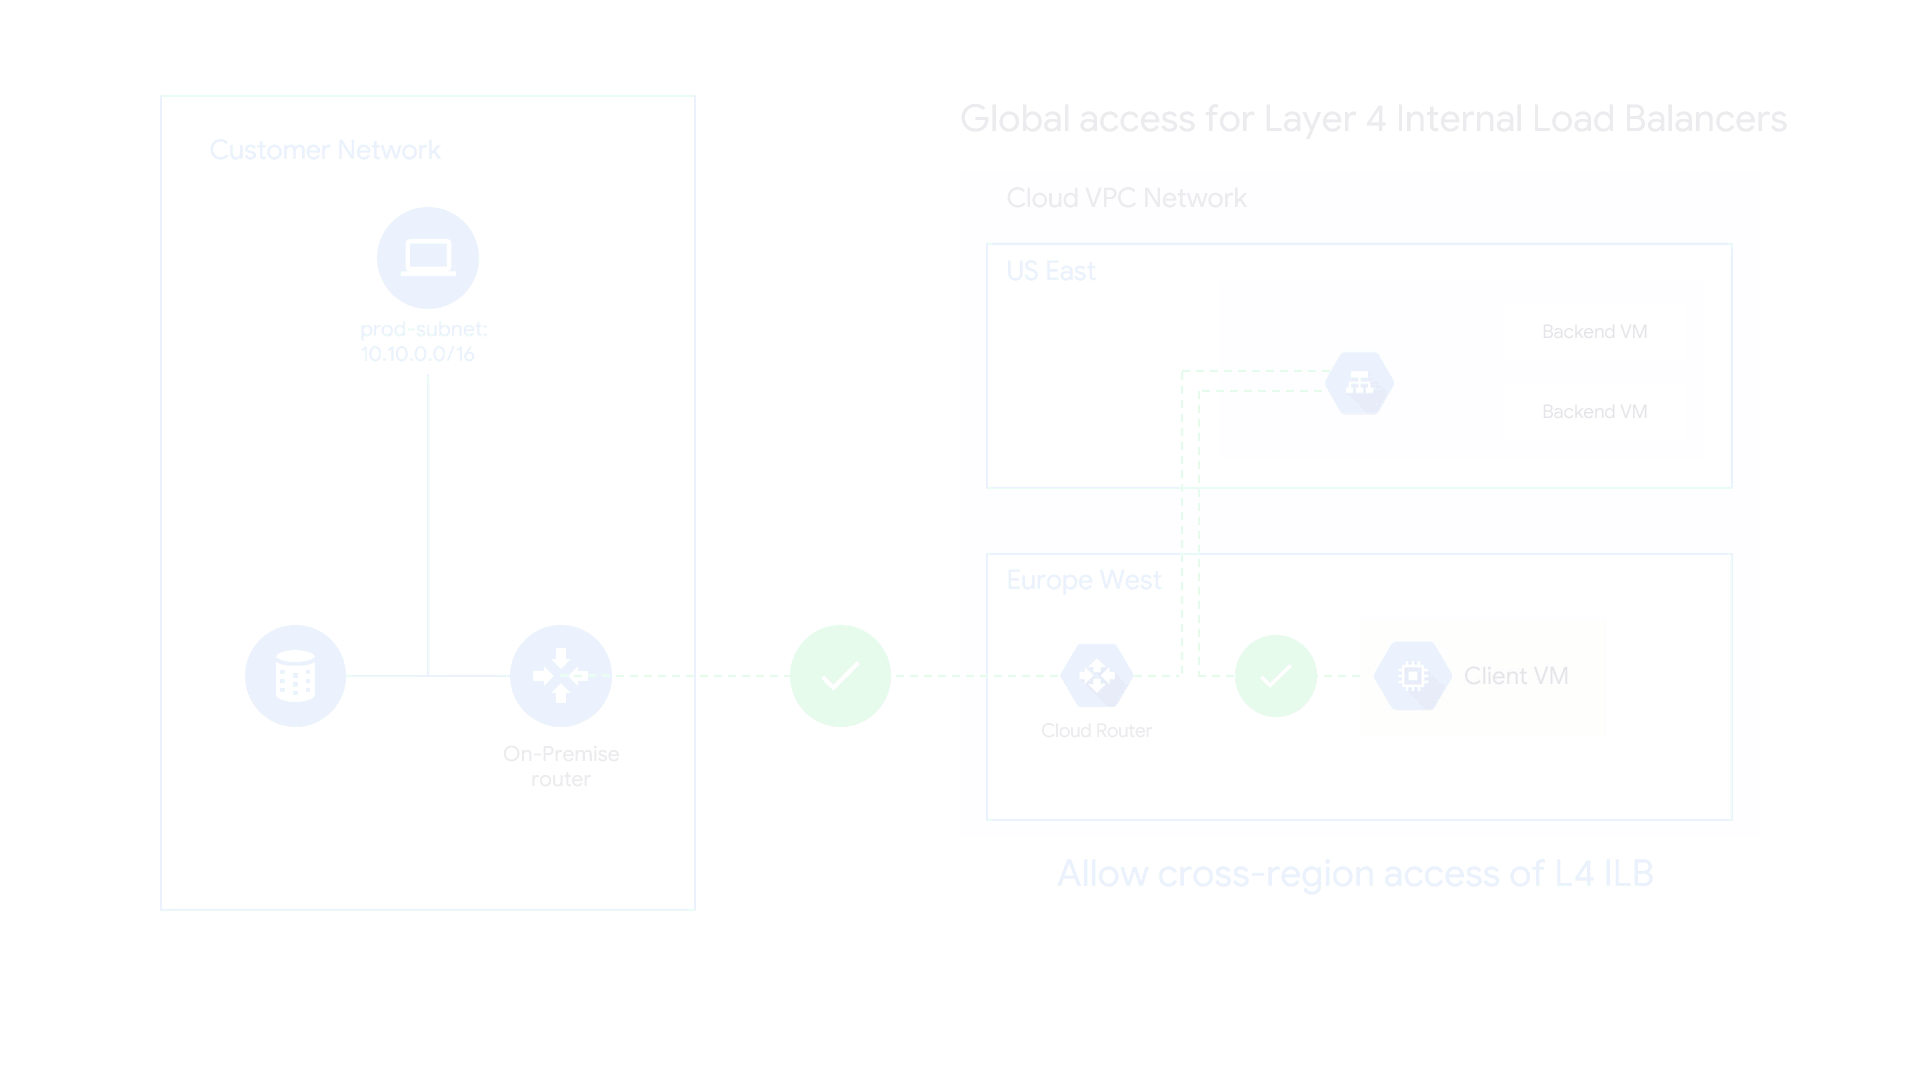
Like many Google Cloud customers, you probably have workloads that need to be private without access to and from the public internet. For scaling and resilience of  those workloads, we offer regional layer-4 Internal Load Balancing (L4 ILB), and we’ve recently added two new L4 ILB features –  ILB global access and  ILB as next-hop with multi-NIC support for third-party appliance integration that  deliver greater availability, scale and ease of management. L4 ILB global access We have added a new global access feature for our L4 Internal load-balancer. While your L4 load-balancer’s backend instances are still in the same region as the L4 ILB, your clients can now access the L4 ILB from any region. This also allows your on-prem clients to access the load balancer, from any region via VPN or a Cloud Interconnect. By multi-homing via VPN or an interconnect to multiple regions, you now have highly available access to the services front-ended by your internal load balancer. As illustrated above, if you lose VPN connectivity from your on-premises network in, say, Boston to Google Cloud region US East, you can still access the L4 ILB in US East via the backup VPN connection from Boston to Europe West. We’re actively working on integrating L4 ILB global access into multiple services: Support for Kubernetes is available in 1.16 release, and Cloud SQL will also support L4 ILB to allow global access to a Cloud SQL database from within the Google Cloud network.A key enabler for the global access feature was incorporating Hoverboard into L4 ILB, which increased the number of L4 ILB Forwarding Rules supported and enables rapid provisioning of these load-balancers. L4 ILB global access was an oft-requested feature by our customers, many of whom beta-tested the feature. CoreLogic, a leading global property information services company, has this to share about L4 ILB global access: “With our deep data, analytics and data-enabled solutions spread across multiple GCP regions in Europe, Australia, and the United States, we leveraged the reach, scale and simplicity of Google’s global network and Internal Load Balancer’s global access to deliver unique insights to our users.” – Steven Myers, Cloud Platform Services and Infrastructure Build Leader, CoreLogic Third-party multi-NIC appliance integrationYou currently need to set up high availability for third-party appliances using the mechanism of routing, which is both complicated and limited in its high-availability capabilities. You have to stitch individual appliance-instances via a route, monitor them and withdraw each route as the instance goes away. We are excited to announce the availability of ILB as next-hop, making it easy to integrate these appliances with high availability and scale out. Simply configure a static route in Google Cloud that sets the next-hop to an Internal Load Balancer, which load-balances traffic to a pool of health-checked third-party VM appliances. The destination IP range can be a default route 0/0, an RFC 1918 prefix, or a non-GCP public IP range owned by you.  In addition, we removed the constraint for L4 ILBh which restricted you to only load-balance to primary NIC0 interface of a VM instance. You can now incorporate multi-NIC VM appliances, with high availability.Several customers are using next-hop support with ILB to easily incorporate third-party appliances, such as those from Palo Alto Networks, into their deployments in Google Cloud. Here is what Palo Alto Networks shared:  “Our customers are able to improve the scalability and availability of their inline threat prevention and network security protections by using Google Cloud’s ILB as next-hop with multi-NIC support to distribute the load across their VM-Series Virtual Next-Generation Firewalls. This helps customers protect outbound and east-west traffic, as well as enabling consistent security for hybrid cloud environments.”  – Mukesh Gupta, VP VM-Series, Palo Alto Networks We brought you ILB global access and ILB as next-hop to offer greater availability, scale and ease of management of your services and virtual appliances. We hope you give these features a try. Start with the documentation on global access, read an overview on L4 ILB as next-hop, walk through a multi-nic configuration, and deploy it in Google Cloud. We look forward to your feedback!
Quelle: Google Cloud Platform

Building an End-to-End 5G Cloud Native Network with OpenShift

In case you missed KubeCon 2019 in San Diego, the CNCF have been very diligent about putting the talks up online. That includes the 5G focused keynote delivered by Azhar Sayeed with Heather Kirksey (Linux Foundation) and Fu Qiao (China Mobile). A short summary of the talk is below, and naturally, the video is above.
It’s no secret that Kubernetes has gained significant traction in the cloud and enterprise software ecosystem, but less widely known is how this momentum is now moving into global telco networks as the next major area of adoption. Building on the momentum from a live keynote demo In Amsterdam last fall (see the demo here), a team made up of volunteers from several project communities, companies, and network operators has taken a cloud native approach to developing an E2E 5G network demonstration built on open source infrastructure. The demo will use a live prototype running in labs around the world using k8s and other open source technologies to deliver a fully containerized 5G-network on stage in San Diego. The demo will showcase both how the telecom industry is using cloud native software to build out their next gen networks, and also show solution providers what’s possible in this exciting new space.
The post Building an End-to-End 5G Cloud Native Network with OpenShift appeared first on Red Hat OpenShift Blog.
Quelle: OpenShift