SpaceX: Oberstufe von Falcon 9 schlägt in Kürze auf dem Mond ein
In wenigen Tagen soll ein Teil einer Falcon-9-Rakete auf dem Mond aufschlagen. Der Zeitpunkt steht inzwischen sehr genau fest. (Falcon-9, Nasa)
Quelle: Golem

In wenigen Tagen soll ein Teil einer Falcon-9-Rakete auf dem Mond aufschlagen. Der Zeitpunkt steht inzwischen sehr genau fest. (Falcon-9, Nasa)
Quelle: Golem

Wer seine Daten zentral und sicher per NAS-Server speichern möchte, profitiert von starken Angeboten. Das Ugreen NASync DXP2800 GT gibt es aktuell zum Tiefstpreis. (Technik/Hardware, Storage)
Quelle: Golem

Die Pläne für eine Verschmelzung der Deutschen Telekom und T-Mobile US sind vom US-Management abgelehnt worden. Auch institutionelle Investoren und US-Regulierungsbehörden haben Bedenken. (Telekom, Mobilfunk)
Quelle: Golem
AWS Lambda now supports Java 8, Java 11, and Java 17 runtimes on Amazon Linux 2023 (AL2023), available as both managed runtimes and container base images. These new runtimes enable customers running Lambda functions on Java 8, 11, or 17 to migrate from Amazon Linux 2 (AL2) to AL2023 without requiring a simultaneous Java version upgrade. The existing Lambda runtimes for Java 8, 11 and 17 run on AL2, which reached end of life on June 30, 2026. To maintain support coverage and SLA eligibility, customers must migrate their functions to an AL2023-based runtime. AWS recommends that customers upgrade to Java 21 or Java 25 on AL2023 as the preferred migration path. These runtimes offer the latest language features and performance improvements. For customers who are not yet ready to upgrade their Java version, the new Java 8, 11, and 17 runtimes on AL2023 provide an alternative forward path. In addition, the existing AL2-based Lambda runtimes for Java 8, 11, and 17 will remain supported and continue to receive patches for critical and selected important security issues until June 30, 2027, giving customers a full year after AL2’s end of life to complete their migration. The Java 8, 11, and 17 runtimes on AL2023 are available in all AWS Regions where Lambda is available, including the AWS GovCloud (US) Regions and the China Regions. To learn more about AL2023 support in Lambda, see our blog post. For customers ready to upgrade to Java 21 or Java 25, you can use AWS Transform custom to assist with the migration. To learn more about Lambda runtimes, visit the Lambda runtimes documentation.
Quelle: aws.amazon.com
Amazon RDS for Oracle now offers 1-year and 3-year Reserved Instances for R8i and M8i instances with up to 53% cost savings compared to On-Demand prices. These instances are powered by custom Intel Xeon 6 processors, available only on AWS, delivering the highest performance and fastest memory bandwidth among comparable Intel processors in the cloud. R8i and M8i instances offer up to 15% better price-performance and 2.5x more memory bandwidth compared to previous generation Intel-based instances. Reserved Instance benefits apply to both Multi-AZ and Single-AZ configurations. This means that customers can move freely between configurations within the same database instance class type, making them ideal for varying production workloads. Amazon RDS for Oracle Reserved Instances also provide size flexibility for the Oracle database engine under the Bring Your Own License (BYOL) licensing model. With size flexibility, the discounted rate for Reserved Instances will automatically apply to usage of any size in the same instance family. Customers can now purchase Reserved Instances for Amazon RDS for Oracle in all AWS regions where R8i and M8i instances are available except the South America (São Paulo) Region. For information on specific Oracle database editions and licensing options that support these database instance types, refer to the Amazon RDS user guide. To get started, purchase Reserved Instances through the AWS Management Console, AWS CLI, or AWS SDK. For detailed pricing information and purchase options visit Amazon RDS for Oracle Pricing.
Quelle: aws.amazon.com

Was bleibt vom KI-Boom, wenn überzogene Versprechen, Bewertungen und Geschäftsmodelle verschwinden? Ihr habt uns eure Meinung gesagt. (KI, Börse)
Quelle: Golem

Open Weight statt Cloud: Qwen 3 TTS bringt hochwertige deutsche Sprachsynthese auf den eigenen Rechner. Von Mathias Küfner (KI, Raumklang)
Quelle: Golem

Diese Mobile Wallbox lädt mit bis zu 11 kW über CEE-Stecker und Typ-2-Kabel. Liegt bei Amazon nur rund fünf Euro über dem Bestpreis. (Elektromobilität, Elektroauto)
Quelle: Golem
Eliminate Stored Credentials in Your CI/CD Pipelines
TL;DR: Docker now supports OpenID Connect (OIDC) for GitHub Actions. Your workflows can authenticate with short-lived, per-run tokens instead of stored PATs or OATs. No secrets to rotate, no credentials to leak.
GitHub OIDC connections are available to organizations with Docker Team, Docker Business, or Docker Hardened Images (DHI) subscriptions, as well as organizations enrolled in the Docker Sponsored Open Source Program (DSOS).
Table of contents
The problem with stored credentials
Who should use this
How OIDC connections work
Getting started
What doesn’t change
Learn more
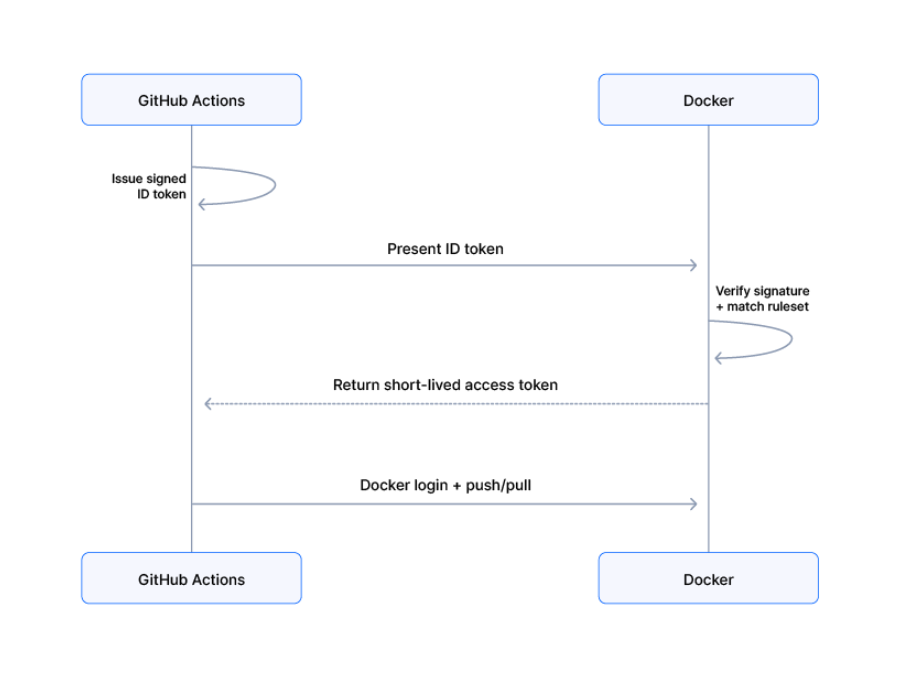
OIDC token exchange flow between GitHub Actions and Docker
The problem with stored credentials
Every GitHub Actions workflow that pushes or pulls images from Docker Hub authenticates with a personal access token (PAT) or organization access token (OAT) stored as a GitHub secret. These credentials are long-lived. Someone has to remember to rotate them. A leaked token grants access to your registry — pulling private images, pushing malicious ones — and that access persists until someone discovers and revokes it. Rotation is manual and does not scale. As pipelines multiply, so do the credentials that need tracking, and stale tokens are a common audit finding.
Who should use this
GitHub issues a signed identity token (a JWT) that encodes the repository, branch, environment, and other metadata about the workflow run.
The workflow calls docker/login-action, which presents this token to Docker.
Docker verifies the token’s signature against GitHub’s public key registry and checks it against rulesets configured in the Admin Console.
If the token matches a ruleset, Docker returns a short-lived access token scoped to the resources defined in that ruleset.
docker/login-action uses this token to authenticate to Docker Hub. From there, docker pull, docker push, and docker build commands work as usual.
The entire exchange happens without any stored secrets, API keys, or access tokens. The short-lived Docker access token expires in minutes and cannot be reused.
This is the same pattern that AWS and GCP already use for cloud resource access (AWS OIDC for GitHub Actions, GCP Workload Identity Federation). Docker is applying it to container registry access.
Getting started
Setup is a one-time connection in Docker Home plus a small update to your workflow YAML.
Step 1: Create a connection
Sign in to Docker Home, select your organization, and navigate to OIDC connections. Select Create OIDC connection and configure the rulesets that control which repositories, branches, and workflows can access which Docker Hub resources. You can create up to five rulesets per connection. When a workflow triggers an OIDC exchange, Docker checks the token against every ruleset defined in your connection. If a ruleset’s conditions are satisfied, Docker grants access based on the parameters set by that ruleset.
Rulesets use OIDC subject claims to match incoming tokens. You can pin to specific repos and branches as a recommended security best practice:
repo:my-org/my-repo:ref:refs/heads/main — only the main branch of a specific repo
repo:my-org/my-repo:ref:refs/heads/release-* — all release branches
repo:my-org/my-repo:* – all branches of this repo
repo:my-org/* — any repo in the organization (not recommended)
Copy the connection ID when you are done.
Note: GitHub repositories created after July 15, 2026 use immutable identifiers for default subject claims. For example: repo:octocat@123456/my-repo@456789:ref:refs/heads/main. See the GitHub changelog for more details.
Step 2: Update your workflow
Update your GitHub Actions workflow. Replace <YOUR_CONNECTION_ID> with the ID from the previous step and <YOUR_ORG_NAME> with your Docker organization name:
permissions:
contents: read
id-token: write
steps:
– name: Docker login
uses: docker/login-action@v4 # v4.5.0+
with:
username: <YOUR_ORG_NAME>
env:
DOCKERHUB_OIDC_CONNECTIONID: <YOUR_CONNECTION_ID>
The id-token: write permission lets the workflow request a GitHub OIDC token. The docker/login-action handles the token exchange and Docker login in a single step when DOCKERHUB_OIDC_CONNECTIONID is set. From there, docker pull, docker push, and docker build commands work as usual.details of the incoming claim sub value, which you can use to diagnose why the connection failed.
Step 3: Verify the OIDC connection works
Run your workflow and confirm it completes successfully. If you encounter an error, the Failures tab of the OIDC connection page will show the details of the incoming claim sub value, which you can use to diagnose why the connection failed.
Step 4: Remove the stored credential
After verifying your workflow runs successfully with OIDC, remove the old PAT or OAT from your GitHub repository secrets. You no longer need it.
Migration Checklist
Create a connection
Update your workflow
Verify the OIDC connection works
Remove stored credentials
What doesn’t change
Existing PATs and OATs keep working. Organizations can migrate workflows to OIDC connections at their own pace.
Images, registries, and build workflows are unchanged. OIDC connections only replace the authentication step; everything downstream is the same.
Local development and non-GitHub CI still use PATs and OATs. OIDC connections are the recommended replacement for GitHub Actions specifically. Other CI providers will follow based on demand.
Learn more
Learn more about OpenID Connect
Visit Docker Home to get started
Read the documentation
Quelle: https://blog.docker.com/feed/
Starting today, Amazon Elastic Compute Cloud (Amazon EC2) C7i instances powered by custom 4th Gen Intel Xeon Scalable processors (code-named Sapphire Rapids) are available in Europe (Milan) and Canada West (Calgary) regions. These custom processors, available only on AWS, offer up to 15% better performance over comparable x86-based Intel processors utilized by other cloud providers. C7i instances deliver up to 15% better price-performance versus C6i instances and are a great choice for all compute-intensive workloads, such as batch processing, distributed analytics, ad-serving, and video encoding. C7i instances offer larger instance sizes, up to 48xlarge, and two bare metal sizes (metal-24xl, metal-48xl). These bare-metal sizes support built-in Intel accelerators: Data Streaming Accelerator, In-Memory Analytics Accelerator, and QuickAssist Technology that are used to facilitate efficient offload and acceleration of data operations and optimize performance for workloads. To learn more, visit the EC2 C7i instances Page.
Quelle: aws.amazon.com






