TinyGPU v2.0: 240.000 Transistoren reichen für 3D-Grafik
Eine winzige GPU mit nur rund 240.000 Transistoren rendert erstmals 3D-Grafik auf echter Hardware. Schnell ist sie nicht. (Grafikkarten, AMD)
Quelle: Golem

Eine winzige GPU mit nur rund 240.000 Transistoren rendert erstmals 3D-Grafik auf echter Hardware. Schnell ist sie nicht. (Grafikkarten, AMD)
Quelle: Golem
A new report from Omdia focuses on security issues in the software supply chain, how organizations are responding, and where the biggest gaps remain
In the heat map of cybersecurity vulnerabilities today, among the most intense hot spots is the software supply chain. In fact, it was the shift of the modern attack surface away from isolated systems to the software supply chain that connects them—and Docker’s role in safeguarding that interconnected reality—that first drew me to Docker.
So when Omdia recently released a report, with Docker among its sponsors, that laid out in detail the extent to which the software supply chain is under siege, I wanted to share some highlights.
Key data points
Here are some data points that caught my attention:
Over three-fourths of organizations experienced a software supply chain incident in the preceding 12 months.
AI tech was the top-ranked supply chain risk (40%), ahead of third-party and open-source code (39%), and software dependencies (38%).
Nearly half (45%) of orgs do not feel they have robust software supply chain security, compared to 55% who do.
More than half of orgs (51%) rate secure containers as very effective in securing third-party and open-source code components.
Shifting security left so that developers can secure their code is a high priority for 98% of organizations—and for 32% of those, it’s their top application security priority.
Third-party code and AI usage expand attack surface
A key finding was that increasing usage of third-party code and AI adoption pose security risks that organizations need to address.
Building applications using third-party libraries, open source dependencies, and AI-generated code saves developers a ton of time, so it’s no surprise this trend is on the rise. But it’s code they didn’t write, and as these time-saving inputs keep growing, so do the attack surfaces they expose.
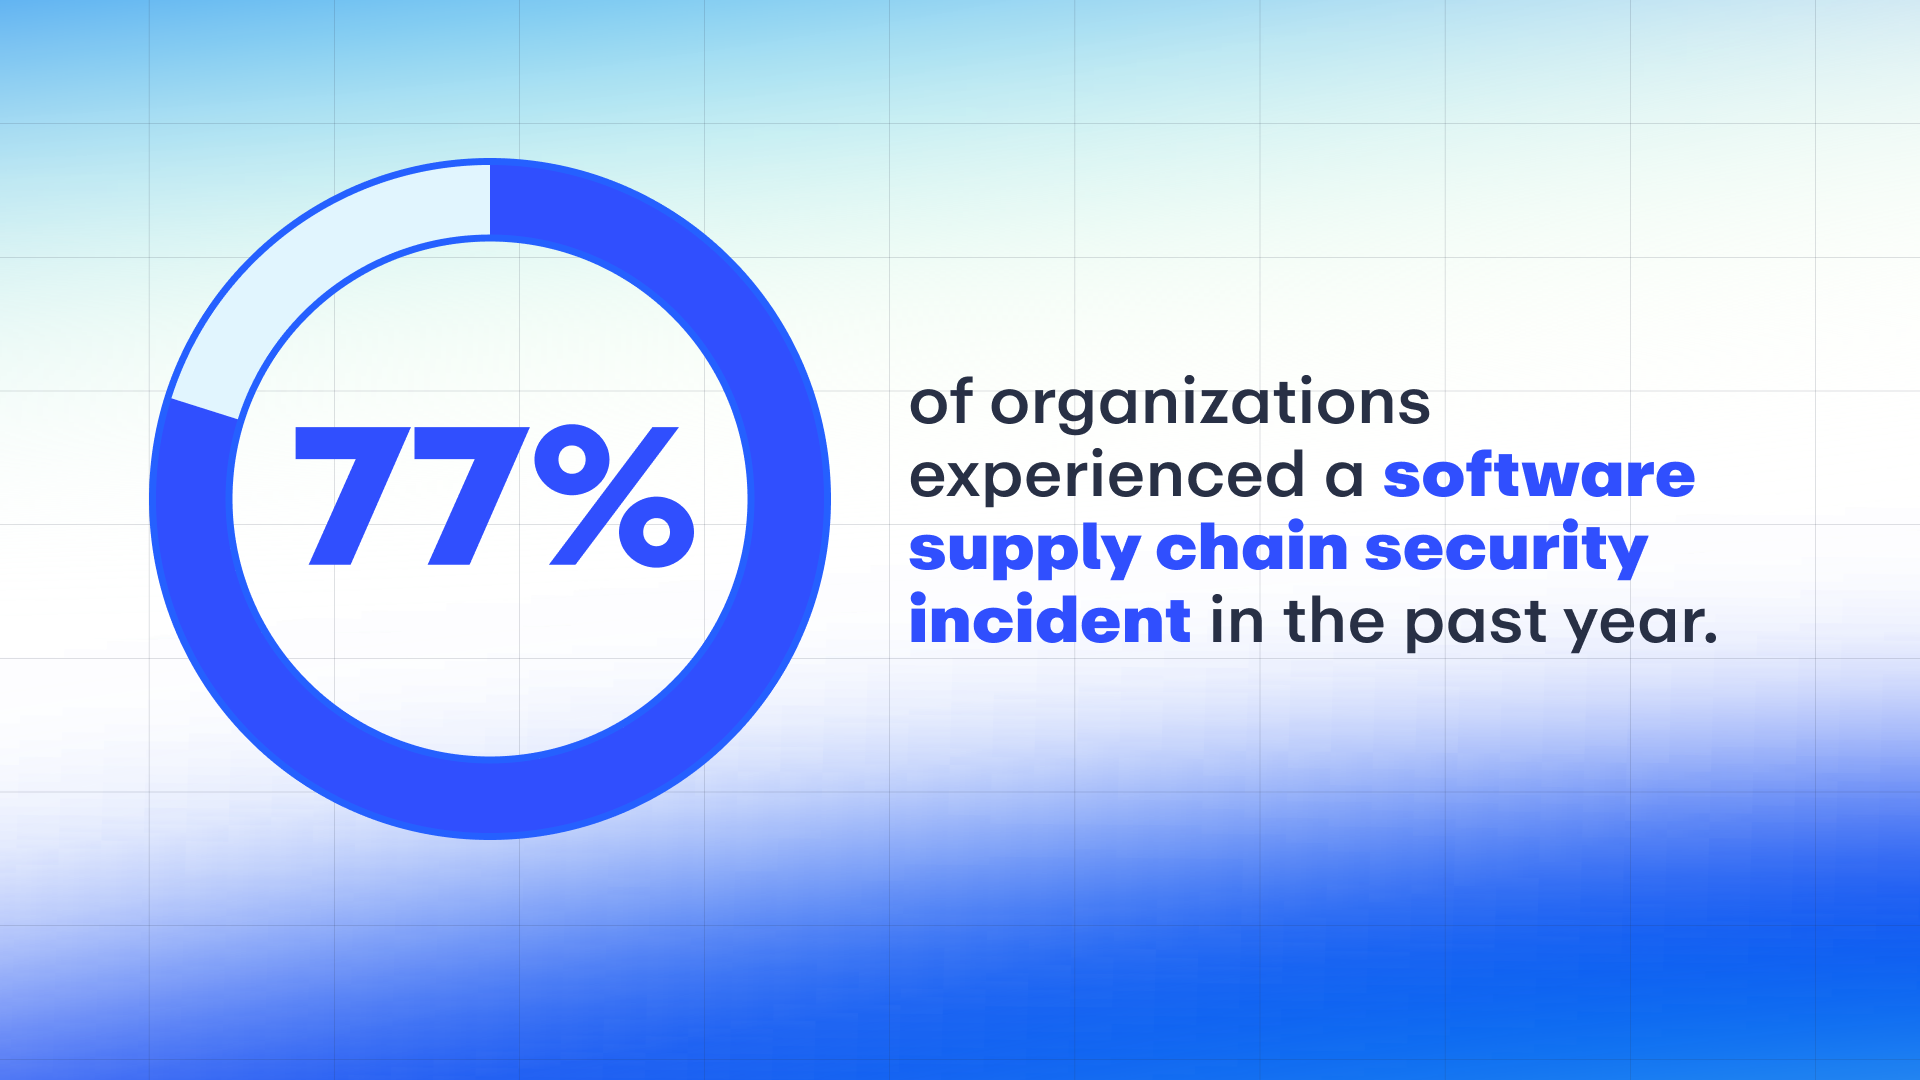
77% of organizations reported experiencing a software supply chain incident in the 12 months prior to the survey (carried out in February 2026).
Notably, the most common attacks (38%) involved exploits that took advantage of known vulnerabilities in third-party software.
Source: Omdia Research Report, Securing the Software Supply Chain: Strategic Approaches to Support Scaling Development with AI Adoption, April 2026
Third-party code usage trending upward
Third-party code usage, including open-source software, isn’t going away. In fact, it’s gaining momentum.
38% of organizations report that more than half of their total software code comes from third-party sources—expected to jump to 58% of organizations in 12 months.
Similarly, 31% of orgs report more than half of their code is comprised of OSS—expected to jump to 51% of orgs in 12 months.
The report found that OSS is vital to developers and must be supported, and that orgs are either confident (50%) or completely confident (31%) that their developers are only using secure OSS.
AI tops security concerns
It should come as no surprise that, as devs increasingly use AI tech to develop software, AI tops the list of concerns around software supply chain risks (40%), ahead of third-party code (39%) and software dependencies (38%).
In the rapidly evolving threat landscape, new types of cyber attacks are emerging that are very different from CVEs (Common Vulnerabilities and Exposures). Take the Shai-Hulud campaign pioneered by TeamPCP, which automates and scales software supply chain attacks using stolen credentials to weaponize well-known packages and inject infostealers deep into the ci/stack or developer laptops.
Using third-party software including OSS is problematic for orgs on multiple fronts. The most common challenges are around vulnerability management.
Orgs worry about vulnerability remediation (39%) and/or identifying vulnerabilities in the code (36%).
And, because AI tools often pull from third-party and OSS code, 35% worry about AI increasing or generating vulnerable code.
Current solutions often fall short
There appears to be a fair degree of awareness around the need to secure the software supply chain. While many orgs are looking to bolster their software supply chain security, nearly half (45%) do not feel they have robust security in this area, compared to 55% who do.
At the risk of tooting our own horn, secure container services or libraries of hardened container images was the highest-rated tool for being “very effective” in securing third-party and OSS code components. In fact, out of 11 security tool categories, it was the only one rated as very effective by a majority of organizations (51%).
SBOMs play key role in boosting security
Another key finding was that effective inventory and SBOM (software bill of materials) tools can lead to measurably better security outcomes.
SBOMs are essential because they eliminate structural blindness, providing transparency into the hundreds of third-party components that form the “ingredients” of a modern application. They are even more effective when paired with a VEX statement (Vulnerability Exploitability eXchange), which tells customers whether flagged vulnerabilities pose a risk or not—potentially saving security teams thousands of hours spent chasing “ghost” vulnerabilities.
According to the report, SBOMs help orgs manage software supply chain risk in a range of ways, including more efficient vulnerability mitigation (73%), implementing security controls and processes to mitigate risk (72%), and helping meet compliance regulations (68%).
However, among organizations that generate an SBOM as part of their application development processes, less than half (42%) do so as a mandatory part of the process for all applications. More than half (55%) generate SBOMs on a case-by-case basis.
Producing SBOMs and understanding code composition ranked fourth among challenges orgs face with using third-party software including OSS.
Action needed—fast
The report underscores the need for preventative measures and rapid response in the face of a quickly evolving threat landscape. Among the impacts of software supply chain incidents are the following:
Nearly half of orgs (46%) faced unauthorized access to applications and data.
More than one-third had SLAs impacted by remediation steps (37%) and/or experienced stolen developer credentials, secrets, or keys (35%).
Organizations also suffered loss of data, introduction of malware and ransomware, and fines for noncompliance.
These impacts underscore the need to mitigate risk as early as possible in the development lifecycle—ideally catching and remediating issues before applications are deployed.
Investment plans and shifting security left
When asked about their spending plans in the face of these risks, orgs responded as follows:
Nearly two-thirds (62%) expect to make significant investments in software supply chain security.
37% anticipate making more modest investments.
A final key finding was that investment plans prioritizing AI require collaboration across teams. That’s largely because the job of securing the software supply chain increasingly falls to those on the front line: developers.
In fact, shifting security left so that developers can secure their code is a high priority for 98% of organizations—and for 32% of those, it’s their top application security priority.
The need to support development
One of the more resonant issues surfaced in the report was the need to support developers on the front lines. Despite the support for shifting security left to eliminate the security team as a bottleneck for remediating security issues, nearly half (45%) of security teams have only moderate or less influence over security products and processes for developers.
And while the majority of respondents believe their developers are mostly (38%) or completely (45%) comfortable taking on security responsibilities, orgs whose developers are less comfortable need to remove as much friction as possible from the process—for example, by making sure security tasks are not disruptive to the development process, and that security tools roll out consistently across development teams and work within development workflows.
The software supply chain isn’t getting simpler, and neither are the threats targeting it. If you’re evaluating how your organization can better secure third-party code, AI-generated code, and open source dependencies, the full Omdia report offers a deeper look at the trends, data, and practical recommendations shaping software supply chain security. Download the report to see where your organization stands and where to focus next.
Quelle: https://blog.docker.com/feed/
Amazon Relational Database Service (Amazon RDS) for SQL Server now supports Bring Your Own Media (BYOM) in 10 additional AWS Regions: Asia Pacific (Taipei, Hyderabad, Jakarta, Malaysia, Melbourne, New Zealand, Thailand), Europe (Milan, Spain), and Mexico (Central). With BYOM, you can adopt Amazon RDS as a managed database service and reuse your existing Microsoft SQL Server licenses with active Software Assurance, through Microsoft’s License Mobility program. BYOM is supported on SQL Server 2019, 2022, and 2025. Amazon RDS for SQL Server BYOM is integrated with AWS License Manager so you can track license usage across your AWS environment for compliance. To learn more, see Bring Your Own Media (BYOM) for RDS for SQL Server. For pricing and regional availability, see Amazon RDS for SQL Server Pricing.
Quelle: aws.amazon.com
AWS announces the general availability of Amazon EC2 Storage Optimized I8g instances in AWS Europe (Paris) and Asia Pacific (Jakarta) regions. I8g instances are powered by AWS Graviton4 processors and offer the best compute performance in Amazon EC2 for storage-intensive workloads. I8g instances use the third generation AWS Nitro SSDs, local NVMe storage that deliver up to 65% better real-time storage performance per TB while offering up to 50% lower storage I/O latency and up to 60% lower storage I/O latency variability compared to I4g instances. These instances are built on the AWS Nitro System, which offloads CPU virtualization, storage, and networking functions to dedicated hardware and software enhancing the performance and security for your workloads.
Amazon EC2 I8g instances are designed for I/O intensive workloads that require rapid data access and real-time latency from storage. These instances excel at handling transactional, real-time, distributed databases, including MySQL, PostgreSQL, Hbase and NoSQL solutions like Aerospike, MongoDB, ClickHouse, and Apache Druid. They’re also optimized for real-time analytics platforms such as Apache Spark, data lakehouse and AI LLM pre-processing for training. I8g instances are available in eleven different sizes including two metal sizes, 1.5 TiB of memory, and 45 TB local instance storage. They deliver up to 100 Gbps of network performance bandwidth, and 60 Gbps of dedicated bandwidth for Amazon Elastic Block Store (EBS).
To learn more, visit Amazon EC2 I8g instances. To begin your Graviton journey, visit the Level up your compute with AWS Graviton page. To get started, see AWS Management Console, AWS Command Line Interface (AWS CLI), and AWS SDKs.
Quelle: aws.amazon.com
AWS Application Load Balancer (ALB) and Network Load Balancer (NLB) now support new TLS-based security policies that comply with RFC 9151 TLS server requirements for Commercial National Security Algorithm (CNSA) 1.0 suite requirements. These policies implement the cryptographic requirements defined by the US National Security Agency (NSA) for secure communications using TLS 1.2 and TLS 1.3 protocols. Customers who are required to meet CNSA 1.0 TLS security requirements can now use ALB and NLB with RFC 9151 compliant security policies. Broader interoperability policies are also supported, allowing you to implement CNSA by default while maintaining compatibility with non-CNSA clients during their transition to RFC 9151 compliance, minimizing service disruption. This feature is available for ALB and NLB in all AWS Commercial Regions, the AWS GovCloud (US) Regions, and the China region at no additional cost. To use this capability, update your existing ALB HTTPS listeners or NLB TLS listeners to a RFC 9151 compliant security policy, or select a compliant policy when creating new listeners through the AWS Management Console, CLI, API, or SDK. To learn more, visit the ALB User Guide and NLB User Guide documentation. Get started with Elastic Load Balancing.
Quelle: aws.amazon.com
Starting today, Amazon Elastic Compute Cloud (Amazon EC2) C8g instances are available in AWS Europe (Paris), AWS Africa (Cape Town), AWS Israel (Tel Aviv), and AWS Canada West (Calgary) regions. These instances are powered by AWS Graviton4 processors and deliver up to 30% better performance compared to AWS Graviton3-based instances. Amazon EC2 C8g instances are built for compute-intensive workloads, such as high performance computing (HPC), batch processing, gaming, video encoding, scientific modeling, distributed analytics, CPU-based machine learning (ML) inference, and ad serving. These instances are built on the AWS Nitro System, which offloads CPU virtualization, storage, and networking functions to dedicated hardware and software to enhance the performance and security of your workloads.
AWS Graviton4-based Amazon EC2 instances deliver the best performance and energy efficiency for a broad range of workloads running on Amazon EC2. These instances offer larger instance sizes with up to 3x more vCPUs and memory compared to Graviton3-based Amazon C7g instances. AWS Graviton4 processors are up to 40% faster for databases, 30% faster for web applications, and 45% faster for large Java applications than AWS Graviton3 processors. C8g instances are available in 12 different instance sizes, including two bare metal sizes. They offer up to 50 Gbps enhanced networking bandwidth and up to 40 Gbps of bandwidth to the Amazon Elastic Block Store (Amazon EBS).
To learn more, see Amazon EC2 C8g Instances. To get started, see the AWS Management Console.
Quelle: aws.amazon.com
The AWS Security Hub Extended plan now includes Supply Chain Security as its 10th security category, with Chainguard and Socket as the curated partners. As developers adopt open-source libraries at scale, security teams need confidence that the packages entering their environments are trustworthy and free from malicious code. With this addition, you can detect and block malicious dependencies before they are built into your applications, with the same streamlined activation and pay-as-you-go pricing as every other Extended category. This brings the Extended plan to 23 curated partner solutions. All solutions are on a single AWS bill and no required long-term commitments.
Security Hub Extended is a plan within AWS Security Hub that helps simplify how you procure, deploy, and integrate a full-stack enterprise security solution across endpoint, identity, email, network, data, browser, cloud, AI, security operations, and supply chain. Security findings from all participating solutions are emitted in the Open Cybersecurity Schema Framework (OCSF) and automatically aggregated in AWS Security Hub. With the Extended plan, you can combine AWS and curated partner solutions to quickly identify and respond to risks that span boundaries.
We will continue to expand the Extended plan based on customer feedback. The two new curated partner solutions are available today in all AWS commercial Regions where Security Hub is available. For a list of supported Regions, see the AWS Region table. For more information about pricing, visit the AWS Security Hub pricing page. To get started, visit the AWS Security Hub console or product page.
Quelle: aws.amazon.com

Die Pläne von Bending Spoons für Airtable folgen dem bekannten Muster früherer Firmenkäufe. (Unternehmen, Wirtschaft)
Quelle: Golem

Mit The Grounds führt FC 27 eine Onlinewelt für bis zu 100 Spieler ein. Sie soll neue Spielmöglichkeiten bieten und den Clubs-Modus beleben. (Fußball, Electronic Arts)
Quelle: Golem

Amazon hat einen Mähroboter mit Garage im Angebot, der mit LiDAR und optischen Sensoren navigiert und auf Sprachbefehle reagiert. (Mähroboter, Segway)
Quelle: Golem






