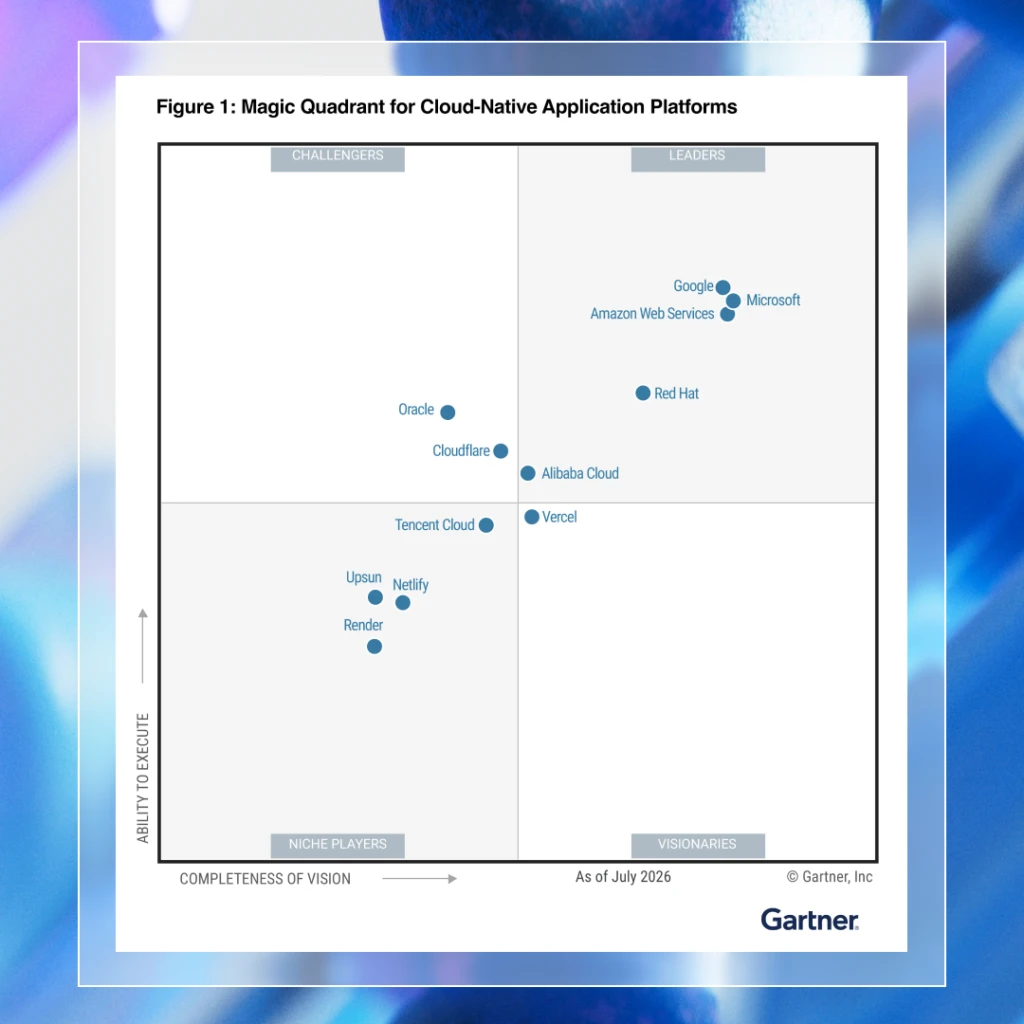
Microsoft has been named a Leader in the 2026 Gartner® Magic Quadrant™ for Cloud-Native Application Platforms, which we believe recognizes the platforms organizations rely on to build, deploy, and operate cloud-native applications at scale. This is our third consecutive year positioned as a Leader in this report.
Read the report
We are proud of this recognition. More importantly, we believe it reflects a shift we see across industries. Cloud-native application platforms are no longer where organizations build and run modern applications. They are becoming the foundation for AI transformation.
The challenge is not a shortage of AI ideas. It is turning those ideas into production systems that can connect to existing applications and data, perform reliably at global scale, and meet the security and governance standards the business already expects. That requires more than a collection of application services. It requires a platform that brings application modernization, AI innovation, operations, and security together.
Microsoft’s cloud-native application platform is designed around that reality. Azure App Service provides a managed foundation for enterprise web applications and modernization. Container Apps runs cloud-native applications, APIs, AI inferencing, and agents without requiring teams to manage infrastructure. Azure Functions provides event-driven execution and integration, while API Management governs APIs, models, and agent tools through a consistent policy layer. Together with Microsoft Foundry, GitHub Copilot, and the shared Azure foundation for identity, networking, observability, and security, these capabilities give organizations one platform for what they already run and what they build next.
Gartner® Magic Quadrant™ graphic for Cloud-Native Applications Platform 2026
Build AI apps and agents faster
Microsoft brings the application runtime and AI toolchain together so developers can build with the model, framework, and architecture that fits the job. Microsoft Foundry provides the models, agent tooling, evaluation, tracing, and safety capabilities needed to take AI systems into production. GitHub Copilot helps developers move faster across the development lifecycle. Azure’s application platform provides the managed runtime, event-driven execution, integration, and API capabilities to turn those systems into applications people can rely on.
This is where platform capabilities matter. Developers can deploy a container directly to a production endpoint with Azure Container Apps Express, and use Azure Functions to expose existing business logic through the Model Context Protocol. More than 1,400 connectors help agents act across enterprise systems without requiring developers to rebuild authentication, retries, and integration logic for every connection.
Azure Container Apps Sandboxes provide the isolated compute that agent platforms run on. The same primitive runs the agent itself, hosts its tools and MCP servers, and executes the code it generates, each in its own microVM, hardware-isolated boundary, with state that survives when the agent pauses. It is the compute layer behind Foundry Agent Service and is available to customers building and operating their own agent platforms on Azure.
The result is a shorter path from an AI idea to a governed application or agent that can deliver on your business goals.
Modernize applications regardless of architecture
AI transformation starts with the application estate organizations already have, not a blank slate. Azure gives teams a practical path to modernize at their own pace. They can move established applications to fully managed Platform as a Service (PaaS) services, containerize where it makes sense, adopt event-driven patterns incrementally, and extend existing business logic so it can participate in AI-powered experiences. App Service Managed Instance helps organizations move complex Windows and .NET applications without requiring a rewrite, while GitHub Copilot app modernization accelerates assessment and remediation. Once modernized, those applications can connect to the same data, AI services, APIs, identity controls, and operational practices as new cloud-native applications.
This flexibility protects the value already in the application estate while creating a foundation for continuous innovation. Organizations do not have to choose between modernizing the core and building for the AI era. The platform makes those efforts part of the same strategy.
Secure, govern, and simplify operations
AI applications raise the operational bar. Agents can call APIs, execute generated code, and interact with sensitive systems at a speed and volume that traditional controls were not designed to manage. Security, governance, and observability cannot be added after deployment. They need to be part of the platform.
Azure provides shared identity, networking, policy, and security controls across the application estate. Azure API Management extends that consistency to APIs, MCP servers, and model endpoints. Its AI gateway capabilities help teams authenticate access, enforce token limits and quotas, balance traffic across models, apply semantic caching, and monitor how AI services are consumed. Azure Container Apps Sandboxes add hardware-level isolation for agent-generated or untrusted code, while confidential computing and Microsoft Defender strengthen protection for sensitive workloads.
Operations also need to keep pace with development. Azure combines global reach with managed scaling across web apps, containers, functions, and APIs. Built-in load balancing, zone redundancy, deployment controls, and integrated observability help teams maintain performance as usage grows. Azure Monitor and Application Insights give teams end-to-end visibility across applications and AI workloads. Azure SRE Agent brings agentic operations into that environment by helping teams investigate incidents, identify root causes, and take auditable remediation actions. Together with GitHub Copilot, these capabilities create a secure and reliable path across the application lifecycle, from development to production operations.
Customer momentum across the platform
Across banking, retail, healthcare, manufacturing, IT, and other industries, organizations are running their most critical applications and their newest AI workloads on the same Azure foundation.
A clean cloud architecture is a prerequisite for AI. You can’t build on top of a weak foundation.
Mike Gibson, Chief Technology Officer, Planet DDS
Planet DDS built that foundation on Azure. It modernized its platform on Azure App Service and cut provisioning time from six weeks to one day, which gives its teams room to invest in the product rather than the plumbing. Replit and Microsoft Azure now put enterprise software building in reach of every Hexaware employee, extending development beyond the people who write code for a living.
That same platform is already running AI in production. Commerzbank runs its agentic AI architecture on Azure Container Apps, where its Ava assistant handles more than 30,000 customer conversations each month and resolves 75% of them autonomously. Ghassan Aboud Group built its Ragin AI platform on Azure Container Apps to deliver agentic customer experiences across its businesses. Levi Strauss and Co. uses Microsoft Foundry to simplify everyday work and accelerate decision-making. These are not experiments running alongside the business. They are AI systems operating inside it.
Taken together, these stories describe one platform doing several jobs at once. It carries existing applications forward, runs new AI and agentic workloads in production, and gives organizations a common foundation to operate both with confidence.
We believe the next generation of applications will be cloud-native, AI-powered, and deeply connected to the systems organizations already rely on. In our view, Microsoft’s position as a Leader for the third consecutive year reinforces our commitment to giving every organization one secure, scalable platform to modernize what it has and build what comes next.
Get started
Wherever you are in your journey, there is a place to begin today.
Building AI apps and agents. Start on Azure Container Apps to build your agentic applications with built-in enterprise security and ultra-fast scale.
Modernizing existing applications. Bring Windows and .NET workloads forward with App Service Managed Instance, and use GitHub Copilot app modernization to accelerate assessment and remediation.
Running event-driven and API-centric workloads. Build with Azure Functions and manage your APIs, MCP servers, and model endpoints through Azure API Management.
Operating with confidence. Add Azure SRE Agent and Azure Monitor to bring agentic operations and end-to-end observability to what you already run.
Microsoft Named a Leader by Gartner®
Learn why Microsoft earned Leader recognition in the 2026 Gartner® Magic Quadrant™ for Cloud-Native Application Platforms.
Read the report
Gartner ® Magic Quadrant™ for Cloud-Native Application Platforms, Mukul Saha, Alex Coqueiro, Prasanna Lakshmi Narasimha, Richard Watson, August 3, 2026.
Gartner does not endorse any company, vendor, product or service depicted in its publications, and does not advise technology users to select only those vendors with the highest ratings or other designation. Gartner publications consist of the opinions of Gartner’s business and technology insights organization and should not be construed as statements of fact. Gartner disclaims all warranties, expressed or implied, with respect to this publication, including any warranties of merchantability or fitness for a particular purpose.
Gartner and Magic Quadrant are trademarks of Gartner, Inc., and/or its affiliates.
This graphic was published by Gartner, Inc. as part of a larger research document and should be evaluated in the context of the entire document. The Gartner document is available upon request from here.
The post Microsoft named a Leader in the 2026 Gartner® Magic Quadrant™ for Cloud-Native Application Platforms appeared first on Microsoft Azure Blog.
Quelle: Azure